Archive 13.07.2026

Page 6 of 8
1 4 5 6 7 8

Wristband enables wearers to control a robotic hand with their own movements

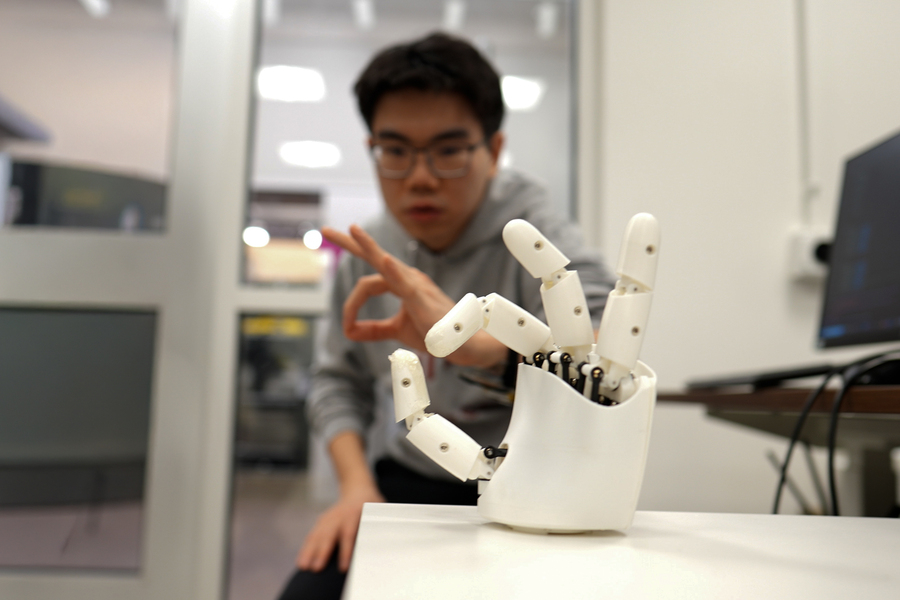
Graduate student Dian Li working with a robotic hand. Credit: Melanie Gonick.

By Jennifer Chu

The next time you’re scrolling your phone, take a moment to appreciate the feat: The seemingly mundane act is possible thanks to the coordination of 34 muscles, 27 joints, and over 100 tendons and ligaments in your hand. Indeed, our hands are the most nimble parts of our bodies. Mimicking their many nuanced gestures has been a longstanding challenge in robotics and virtual reality.

Now, MIT engineers have designed an ultrasound wristband that precisely tracks a wearer’s hand movements in real-time. The wristband produces ultrasound images of the wrist’s muscles, tendons, and ligaments as the hand moves, and is paired with an artificial intelligence algorithm that continuously translates the images into the corresponding positions of the five fingers and palm.

The researchers can train the wristband to learn a wearer’s hand motions, which the device can communicate in real-time to a robot or a virtual environment.

In demonstrations, the team has shown that a person wearing the wristband can wirelessly control a robotic hand. As the person gestures or points, the robot does the same. In a sort of wireless marionette interaction, the wearer can manipulate the robot to play a simple tune on the piano and shoot a small basketball into a desktop hoop. With the same wristband, a wearer can also manipulate objects on a computer screen, for instance pinching their fingers together to enlarge and minimize a virtual object.

The team is using the wristband to gather hand motion data from many more users with different hand sizes, finger shapes, and gestures. They envision building a large dataset of hand motions that can be plumbed, for instance, to train humanoid robots in dexterity tasks, such as performing certain surgical procedures. The ultrasound band could also be used to grasp, manipulate, and interact with objects in video games, design applications, or other virtual settings.

“We think this work has immediate impact in potentially replacing hand tracking techniques with wearable ultrasound bands in virtual and augmented reality,” says Xuanhe Zhao, the Uncas and Helen Whitaker Professor of Mechanical Engineering at MIT. “It could also provide huge amounts of training data for dexterous humanoid robots.”

Zhao, Gengxi Lu, and their colleagues present the wristband’s new design in a paper which appeared in Nature Electronics. Their MIT co-authors are former postdocs Xiaoyu Chen, Shucong Li, and Bolei Deng; graduate students SeongHyeon Kim and Dian Li; postdocs Shu Wang and Runze Li; and Anantha Chandrakasan, MIT provost and the Vannevar Bush Professor of Electrical Engineering and Computer Science. Other co-authors are graduate students Yushun Zheng and Junhang Zhang, Baoqiang Liu, Chen Gong, and Professor Qifa Zhou from the University of Southern California.

Seeing strings

There are currently a number of approaches to capturing and mimicking human hand dexterity in robots. Some approaches use cameras to record a person’s hand movements as they manipulate objects or perform tasks. Others involve having a person wear a glove with sensors, which records the person’s hand movements and transmits the data to a receiving robot. But erecting a complex camera system for different applications is impractical and prone to visual obstacles. And sensor-laden gloves could limit a person’s natural hand motions and sensations.

A third approach uses the electrical signals from muscles in the wrist or forearm that scientists then correlate with specific hand movements. Researchers have made significant advances in this approach, however these signals are easily affected by noise in the environment. They are also not sensitive enough to distinguish subtle changes in movements. For instance, they may discern whether a thumb and index finger are pinched together or pulled apart, but not much of the in-between path.

Zhao’s team wondered whether ultrasound imaging might capture more dexterous and continuous hand movements. His group has been developing various forms of ultrasound stickers — miniaturized versions of the transducers used in doctor’s offices that are paired with hydrogel material that can safely stick to skin.

In their new study, the team incorporated the ultrasound sticker design into a wearable wristband to continuously image the muscles and tendons in the wrist.

“The tendons and muscles in your wrist are like strings pulling on puppets, which are your fingers,” Lu says. “So the idea is: Each time you take a picture of the state of the strings, you’ll know the state of the hand.”

Mapping manipulation

The team designed a wristband with an ultrasound sticker that is the size of a smartwatch, and added onboard electronics that are about as small as a cellphone. They attached the wristband to a volunteer’s wrist and confirmed that the device produced clear and continuous images of the wrist as the volunteer moved their fingers in various gestures.

The challenge then was to relate the black and white ultrasound images of the wrist to specific positions of the hand. As it turns out, the fingers and thumb are capable of 22 degrees of freedom, or different ways of extending or angling. The researchers found that they could identify specific regions in their ultrasound images of the wrist that correlate to each of these 22 degrees of freedom. For instance, changes in one region relate to thumb extension, while changes in another region correlate with movements of the index finger.

To establish these connections, a volunteer wearing the wristband would move their hand in various positions while the researchers recorded the gestures with multiple cameras surrounding the volunteer. By matching changes in certain regions of the ultrasound images with hand positions recorded by the cameras, the team could label wrist image regions with the corresponding degree of freedom in the hand. But to do this translation continuously, and in real-time, would be an impossible task for humans.

So, the team turned to artificial intelligence. They used an AI algorithm that can be trained to recognize image patterns and correlate them with specific labels and, in this case, the hand’s various degrees of freedom. The researchers trained the algorithm with ultrasound images that they meticulously labeled, annotating the image regions associated with a specific degree of freedom. They tested the algorithm on a new set of ultrasound images and found it correctly predicted the corresponding hand gestures.

Once the researchers successfully paired the AI algorithm with the wristband, they tested the device on more volunteers. For the new study, eight volunteers with different hand and wrist sizes wore the wristband while they formed various hand gestures and grasps, including making the signs for all 26 letters in American Sign Language. They also held objects such as a tennis ball, a plastic bottle, a pair of scissors, and a pencil. In each case, the wristband precisely tracked and predicted the position of the hand.
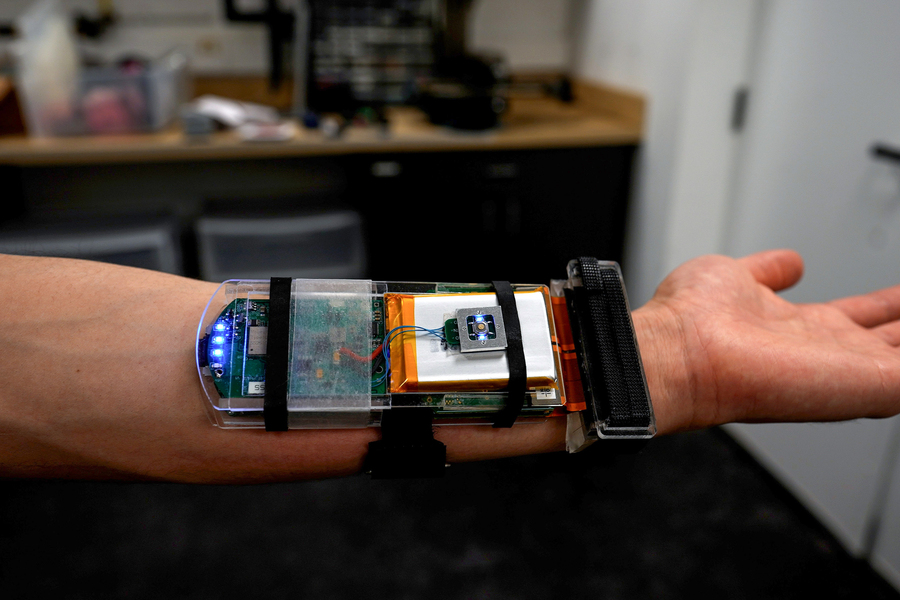
MIT engineers have designed an ultrasound wristband that precisely tracks a wearer’s hand movements in real time. The wristband produces ultrasound images of the wrist’s muscles, tendons, and ligaments as the hand moves. Credit: Melanie Gonick.

To demonstrate potential applications, the team developed a simple computer program that they wirelessly paired with the wristband. As a wearer went through the motions of pinching and grasping, the gestures corresponded to zooming in and out on an object on the computer screen, and virtually moving and manipulating it in a smooth and continuous fashion.

The researchers also tested the wristband as a wireless controller of a simple commercial robotic hand. While wearing the wristband, a volunteer went through the motions of playing a keyboard. The robot in turn mimicked the motions in real-time to play a simple tune on a piano. The same robot was also able to mimic a person’s finger taps to play a desktop basketball game.

Zhao is planning to further miniaturize the wristband’s hardware, as well as train the AI software on many more gestures and movements from volunteers with wider ranging hand sizes and shapes. Ultimately, the team is building toward a wearable hand tracker that can be worn by anyone, to wirelessly manipulate humanoid robots or virtual objects with high dexterity.

“We believe this is the most advanced way to track dexterous hand motion, through wearable imaging of the wrist,” Zhao says. “We think these wearable ultrasound bands can provide intuitive and versatile controls for virtual reality and robotic hands.”

This research was supported, in part, by MIT, the U.S. National Institutes of Health, the U.S. National Science Foundation, the U.S. Department of Defense, and Singapore National Research Foundation through the Singapore-MIT Alliance for Research and Technology.

Fast and Furious: AI Upgrades Abound

*OpenAI Out With Yet Another Upgrade: Meet ChatGPT 5.6, OpenAI’s new AI model, pitched as its most powerful yet.

Simultaneously released with the new AI was ChatGPT Work, an AI agent designed to engage in multi-step tasks without human prodding.

Observes writer Cade Metz: “The release of the more powerful model followed U.S. government efforts to restrict both OpenAI’s and Anthropic’s new AI models over cybersecurity concerns.”

In other news and analysis of AI writing:

*ChatGPT Upgrades Voice to be More Interactive: Fans of voice-driven ChatGPT will most likely welcome GPT-Live, an enhancement of the AI’s voice chops.

Ideally, the upgrade allows ChatGPT to engage in conversation in real-time – including the ability to listen and respond at will.

Observes writer Michael Nunez: “In practice, that translates to a voice assistant that can insert conversational acknowledgments — “mhmm,” “yeah,” “got it” — while you’re still talking.”

*Facebook’s Parent Meta Releases Paid AI for the First Time: Muse Spark – Meta’s new AI model – will be the first AI from the company you’ll need to pay for.

Observes writer Eli Tan: “On tests that measure writing, reasoning, coding and other tasks, Muse Spark performed at or near the same levels as leading models from Anthropic, OpenAI, Google and xAI, according to data shared by the company (Meta).”

So far, Meta is targeting use Muse Spark primarily to developers, rather than chatbot users.

*Meta Releases Muse Image Generator: Facebook’s parent now has its own image generator, designed to compete with similar offerings from ChatGPT and Gemini.

You can find Muse Image on Instagram and WhatsApp.

Observes writer Eli Tan: “Muse Image will replace technology from Midjourney, an AI start-up that Meta previously worked with to generate AI images.”

*SpaceXAI Drops Grok 4.5: Elon Musk’s AI company is out with an upgrade to its AI, dubbed Grok 4.5.

Key strengths of the tech – which will compete with ChatGPT, Gemini, Claude and similar – include knowledge work, coding and agentic tasks, according to the company.

Bonus: Grok 4.5 is also cheaper for developer use than many of its competitors.

*The Case for OpenSource AI: AI OpenSource maker Mistral is warning business users that proprietary AI makers like OpenAI are trying to lock customers into their walled garden technology.

Conversely, OpenSource AI offers companies more options to train AI for their specific use cases — and also often ensures company data run on OpenSource AI remains private, according to Mistral.

Observes writer Alina Maria Stan: “Training your own models is no longer a fringe position. British startup Cosine has rallied BT, HSBC and BAE Systems to build a sovereign UK frontier model, while Palantir has published an AI sovereignty manifesto taking aim at the big labs.”

*U.S. Looking to Block Corporate Use of Chinese AI: Concerned that corporate data processeed on Chinese OpenSource AI could wind-up in the wrong hands, the U.S. government is looking to block use of such AI.

Currently, many U.S. companies use Chinese OpenSource AI, given that it is much less expensive than AI from U.S. AI titans.

Observes writer Daniel Cooper: “It’s not clear if the U.S. could directly impose a sweeping ban on the market’s choice of AI models beyond altering its own procurement rules. And it’s likely the U.S. would not be eager on restricting the use of open source models given the potential first amendment issues that it would create.”

*New AI Offers Automated Q&A for Employee Onboarding: In a novel application of AI, Docsie is out with an AI employee-training program featuring an AI presenter who can answer questions as the presentation is being made.

Ideally, the AI will be able to accurately answer audience questions by sourcing its enterprise knowledge database in real-time.

Observes Philippe Trounev, CEO, Docsie: “Companies already possess years of valuable expertise stored in meetings, webinars, documentation and training videos. AI Avatar Presenter transforms that existing knowledge into interactive AI presenters that can explain concepts, answer questions — and continuously deliver enterprise training without requiring teams to recreate content from scratch.”

*Character.AI Offers Its Own Microdramas: Microdramas –minute-long soap-opera-like dramas already popular on services like TikTok — have come to Character.ai.

The twist: Character.ai microdramas allow users 18 and older to chat with the microdrama characters, ask questions and even engage in roleplay.

Observes writer Ivan Mehta: “The startup is launching three microdramas to start with: A romance series dubbed “Last Summer,” a horror show titled “The Nighttime Game,” and a Hunger Games-like survival microdrama called “Eden Falls.”

*Gearing Up for AI: A Guide: TechRepublic has rolled-out a comprehensive primer on how businesses can get the most from AI.

Key categories offered by the primer include Strategy, Data, Infrastructure, Use Cases and ROI.

Essentially: Its a great info-hub to visit if you’re new to AI and you’re looking for a quick study.

Share a Link:  Please consider sharing a link to https://RobotWritersAI.com from your blog, social media post, publication or emails. More links leading to RobotWritersAI.com helps everyone interested in AI-generated writing.

Joe Dysart is editor of RobotWritersAI.com and a tech journalist with 20+ years experience. His work has appeared in 150+ publications, including The New York Times and the Financial Times of London.

Never Miss An Issue
Join our newsletter to be instantly updated when the latest issue of Robot Writers AI publishes
We respect your privacy. Unsubscribe at any time -- we abhor spam as much as you do.

The post Fast and Furious: AI Upgrades Abound appeared first on Robot Writers AI.

New soft sensor can turn touch into robotic action without electronics

Built from flexible, compliant materials, soft robots are gaining relevance for tasks ranging from minimally invasive surgery to deep-sea exploration but remain held back by a fundamental constraint. To sense their surroundings and react, most soft robots rely on separate electronic sensors, signal-processing circuits and powered actuators, all coordinated by computers. This chain of components adds weight, complexity and points of failure, particularly in wet, hot or high-pressure settings where electronics are highly susceptible to disruption.

New test measures how well humanoid robots handle real-world forces

As technology advances, more is expected from humanoid robots. What were once seen as gimmicks that could walk, if not like us, then close to it, are now pulling their weight and doing more work in places like factories. They are being developed for real work, such as carrying heavy boxes, pushing furniture, pulling heavy objects and wiping tables.

Your agents are using your credentials, and that is the problem

Your agents are using your credentials, and that is the problem

An engineer ships an agent to production. It needs to call an internal API, so it uses the key already sitting in the engineer’s environment. The agent runs. It also now holds every permission that engineer holds.

That is the default state of most agent deployments today. The agent has no identity of its own, so it borrows one. Usually it borrows a human’s, through an API key. The agent works on day one, which is exactly why the problem ships to production unnoticed.

What inheritance actually costs you

Four failures follow from that single shortcut, and they compound.

An agent that inherits a human's key inherits the human's full permission set, and four things break at once.
Figure 1. An agent that inherits a human’s key inherits the human’s full permission set, and four things break at once.

You get privilege escalation. A non-human process now carries a human’s full access. It can reach every system the human can reach, whether the task needs it or not.

You get no scoping. The agent should touch a narrow slice of your systems. Instead it gets everything, because the key was never meant to express “only this.”

You get no attribution. When the agent acts, the audit log shows the human. You cannot separate what the agent did from what the person did. Incident response slows to a crawl, and so does any compliance story you have to tell later.

You get no clean revocation. To shut the agent off, you rotate the human’s key. Now you have broken the human’s own access and every other process that depended on that key. There is no off switch for the agent alone.

A knowledgeable reader will reach for the obvious fixes here. Rotate the key on a schedule. Hand the agent a service account instead. Both miss the real problem.

A passport is the wrong mental model

The instinct is to treat identity as a passport. A passport authenticates who you are and maps you to a fixed set of permissions. Show it at the border, get the access that comes with it. That model works when behavior is predictable inside those permissions. A human with read access to a dataset reads the dataset. A service account that posts to a queue posts to the queue, at the same cadence, every time.

Agents break the assumption underneath the passport. The right question is not “who is this actor.” It is “what is this actor authorized to do right now, for this task.” That is authority, not identity in the passport sense, and the difference is the whole point.

Here is why it matters. An agent is non-deterministic. Give two agents the same permissions and the same goal, and they can take different actions, because each one picks its tool chain at runtime based on its prompt, its context, and the output of whatever called it. The set of actions an agent will actually take is not knowable when you grant its permissions.

That turns design-time least privilege into a design-time answer to a runtime problem. You are deciding, in advance, what an actor may do, when the actor itself decides what to do only once it is running. A static grant cannot keep up with an actor whose behavior shifts on every interaction.

Why your IAM stack does this to you

This is not a configuration mistake. It is a structural assumption baked into identity and access management. The systems you run assume an actor is one of two things: a person, or a long-lived service account with a static permission set. Both are stable. Both do roughly the same thing every day. Your controls, your audit model, and your provisioning flows are all built on that stability.

Agents are neither. They act on behalf of people, so they are not service accounts. They are software that spins up and tears down on its own schedule, so they are not people. They sit in the gap your IAM stack does not have a category for, and the gap is where the credential gets borrowed.

The take-away

If your agents authenticate as the humans who deployed them, you have a privilege-inheritance problem in production right now. Find it before an auditor or an incident does: look for human API keys being used by non-human processes, and for audit logs where you cannot tell agent actions from human ones.

The shallow fix is to stop sharing keys. The real fix is harder. A non-deterministic actor cannot be governed by a static, design-time grant, which means the agent needs an identity built for authority that is decided at runtime, not a passport stamped once at the border.

That raises the obvious question. If the agent needs its own identity, what is that identity actually made of, and is it anything more than the workload identity you already run? That is the next post.

The post Your agents are using your credentials, and that is the problem appeared first on DataRobot.

The Hidden Cost of Automation Downtime: Why IT Reliability Is the Real ROI Driver Behind Robotics and Smart Manufacturing

Manufacturers build the ROI case for automation around labor savings and throughput gains. They rarely build it around the cost of the automation itself going down — and that is usually the number that determines whether the investment actually pays off.

Researchers build missing infrastructure to move AI between robots

Robotics researchers often spend weeks, or even months, simply getting a new robot up and running before they can begin testing new behaviors. Researchers in the Carnegie Mellon University School of Computer Science have developed an open-source software framework designed to eliminate much of that setup work, making it easier to deploy AI systems across different robots without rebuilding software from scratch.

Researchers build missing infrastructure to move AI between robots

Robotics researchers often spend weeks, or even months, simply getting a new robot up and running before they can begin testing new behaviors. Researchers in the Carnegie Mellon University School of Computer Science have developed an open-source software framework designed to eliminate much of that setup work, making it easier to deploy AI systems across different robots without rebuilding software from scratch.

Small aquatic robots that assemble into reconfigurable structures on the water

Most people think of the waterfront as the edge of the city. A team of MIT researchers sees it as a dynamic, Lego-like construction site. Their new system, called "FloatForm," is a swarm of small square robotic boats that assemble themselves into larger structures on the water, break apart and reassemble into something new, all with minimal human direction.

Harvard scientists turn a silicon chip into a DNA writing machine

Scientists have created a silicon chip that can write dozens of DNA sequences simultaneously using electricity and water-based enzymes, offering a cleaner alternative to conventional DNA manufacturing. The breakthrough could eventually support portable DNA-writing devices and even massive DNA data storage, although new chemistry will be needed to scale the technology further.

Scientists used AI to crack one of water’s biggest mysteries

Water’s odd behavior becomes even more dramatic when it is supercooled, but scientists have struggled to compare the many different ways of describing its microscopic structure. Researchers at the University of Osaka used an AI model trained on computer simulations to evaluate 16 different structural descriptors. The system identified the most effective ways to distinguish between water’s two competing liquid states, providing a clearer framework for studying one of nature’s most mysterious substances.

Your identity stack was built for two kinds of actor. Agents are a third.

Your identity stack was built for two kinds of actor. Agents are a third.

An engineer ships an agent to production this week. It needs to call an internal API, so it uses the key already sitting in the engineer’s environment. The agent runs. It also now holds every permission that engineer holds.

That is the default state of most agent deployments today. The agent has no identity of its own, so it borrows one. It works on day one, which is exactly why the problem ships unnoticed. A non-human process is now carrying a human’s full access, and nothing in your audit log can tell the two apart.

This is not a configuration mistake. It is a structural gap. Identity and access management assumes an actor is one of two things: a person, or a long-lived service account with a static permission set. Both are stable. Both do roughly the same thing every day. Your controls, your audit model, and your provisioning flows are all built on that stability.

Agents are neither. They act on behalf of people, so they are not service accounts. They spin up and tear down on their own schedule, so they are not people. They sit in the gap your IAM stack has no category for, and the gap is where the credential gets borrowed.

Why you cannot just patch this

The reason existing IAM cannot simply absorb agents is non-determinism. A service account calls the same endpoints at the same cadence every time. Give two agents the same permissions and the same goal, and they can take different actions, because each one picks its tool chain at runtime based on its prompt, its context, and the output of whatever called it.

The set of actions an agent will actually take is not knowable when you grant its permissions. That turns design-time least privilege into a design-time answer to a runtime problem. You are deciding in advance what an actor may do, when the actor decides what to do only once it is running.

That single fact is the spine of this series. It is why borrowed credentials fail, why scope has to be narrow, why a delegation chain has to stay inspectable, and why authorization cannot be a one-time grant. The question that matters is not “who is this actor.” It is “what is this actor authorized to do right now, for this task.”

If you do nothing else this week

Before the series goes deep, three checks you can run today against any agent already in production.

Look for human API keys being used by non-human processes. If an agent authenticates as the person who deployed it, you have privilege inheritance in production right now.

Check whether your audit logs can separate agent actions from human actions. If they cannot, your incident response and your compliance story both break at the same moment.

Confirm you can shut one agent off without rotating a human’s credential or breaking three other things. If revocation means collateral damage, you do not have an off switch. You have a hostage situation.

None of these is the full fix. They are the floor. Finding where they fail tells you where to start.

What solving this actually looks like

The rest of the series builds the answer in layers, each one resting on the one below it.

It starts with giving the agent a stable, verifiable runtime principal you can authorize against, attribute actions to, and revoke on its own. Then it has to survive contact with reality: agents call tools, tools call other agents, and identity has to stay intact across every hop so you can still answer who originally asked and which actor is making this specific call. The credential the agent uses to make those calls has to stay out of the model itself, where a single prompt injection could read it and send it anywhere. Above that sits the question of where the rules live, and who decides what an agent may do the moment it acts somewhere its own platform does not reach. Underneath all of it runs the lifecycle: an identity you provision, scope, revoke, and re-evaluate while the agent runs, not a record you write once and forget.

Identity is the foundation the rest depends on. Authorization, governance, and observability all sit on top of it. Get identity wrong and nothing above it holds.

Where DataRobot fits

The agent platform from DataRobot treats agent identity as first-class infrastructure, not an afterthought bolted on at deploy time. The direction is the one this series argues for: give each agent its own scoped identity, keep the delegation chain intact and auditable when agents call tools and other agents, govern that identity in one control plane, and federate trust outward to the identity providers and workload identity systems an enterprise already runs.

What is coming

Part one takes apart the borrowed credential. Why inheriting a human’s key is privilege escalation by default, and why the fix is authority decided at runtime, not a passport stamped once at the border.

Part two defines what a first-class agent identity actually is: a distinct principal, scoped permissions, a clear owner, and a kill switch. It also shows how you make that principal trustworthy through attestation, then engages the question a good engineer is already asking. Is this just workload identity? It depends on three invariants, and where they break is where most real fleets live.

Part three follows identity through a delegation chain. RFC 8693 token exchange, the confused deputy you create when you flatten that chain, and the two protocol surfaces where it is preserved or destroyed in practice: MCP and A2A.

Part four keeps the secret out of the model. An agent’s context is attackable, so a prompt injection can read anything in it. That is why the raw credential should never reach the agent’s process. A broker holds it and injects auth at the boundary, and the agent only ever gets a scoped capability.

Part five is about where authorization and governance sit. Govern natively, federate outward, size controls to blast radius, and the frontier nobody has cleanly solved: what happens when an agent acts across trust domains its issuing platform does not control.

Part six treats identity as a lifecycle. Just-in-time, task-scoped credentials, no standing privilege, and continuous runtime authorization. It closes the loop back to non-determinism and leaves you with a six-question audit to run against one real agent.

Part one publishes next. If you want a head start, go find one agent in your environment right now and check whose credentials it is using. That answer is where the series begins.

The post Your identity stack was built for two kinds of actor. Agents are a third. appeared first on DataRobot.

Page 6 of 8
1 4 5 6 7 8