Archive 16.07.2026

Page 5 of 8
1 3 4 5 6 7 8

How Much Does IT Cost to Develop a Medical Chatbot?

How Much Does IT Cost To Develop A Medical Chatbot?

Medical Chatbot: Top Use Cases, Benefits, and Development Cost

Implementation of conversational AI in Medicine and Healthcare has been a trend in the healthcare industry to deliver outstanding care services ever like before. Yes, Artificial Intelligence (AI) has become a promising technology to transform the Patient Care Industry.

The healthcare and medical sector is accelerating digital services and optimizing patient care, especially in emergency conditions, healthcare companies are adopting conversational AI applications like chatbots to monitor and provide 24/7 care services to their patients.

Be it for in-patients or out-patients, AI-powered Healthcare Chatbots are increasingly using across healthcare companies for ensuring better experiences for patients. Today, herein, we have compiled a list of the top benefits of investing in AI chatbots for healthcare and medical services.

What Is A Medical Chatbot?

For delivering convenient and instant care and support services to patients, healthcare service providers are widely using AI-powered medical chatbots. Yes, a medical chatbot is an intelligent and collaborative AI solution developed for better managing routine healthcare functions and delivering virtual care services to patients.

Let’s see a few top applications of medical chatbots:

What Are The Top Use Cases Of Healthcare/Medical Chatbots?

The role of AI-based chatbot solutions for healthcare is prominent for automating various regular tasks like recording logs, reminding medications, generating invoices, and monitoring patients’ health, etc. Offering their patients 24/7 non-stop care services and responding to them instantly on their issues about care services.

  1. 24/7 Virtual Support

It is one of the key roles of AI-based medical and healthcare chatbots. 85% of healthcare service providers are investing in AI chatbots for keeping care services available for patients all the time.

Using Natural Language Processing (NLP) or text-to-speech techniques, interactive and conversational AI chatbots deliver outstanding digital services. Appointment scheduling apps are the best examples that we must discuss here.

Based on the user’s preferred time and specialty, AI chatbots will automatically recommend an available list of doctors and makes booking faster. Hence, such intelligent processes through AI chatbots will make the process virtual and improve the patient experience.

Likewise, top AI chatbot apps in healthcare will also help service providers virtually respond to patient’s issues if any. 

  1. Reduces Caseloads and Improves Productivity 

It is one of the significant healthcare chatbots use cases that we must discuss. By deploying an AI-enabled chatbot in place, healthcare service providers can virtually monitor a few cases anywhere at any time. It will save the physicians valuable time and improves their productivity in handling other emergency cases.

  1. Proper Medication Management

Reminders on medicine intakes and refills are the best Chatbot use cases in the healthcare industry. A conversation AI chatbot plays significant in monitoring and tracking the patient’s medication schedules. Hence, AI medical bots play a key role in sending notifications on medicines intake, dosage, and refills.

Further, a few chatbots are also designed for sending auto reminders on the time to get their kid’s vaccinations and stay on top of the health risks.

  1. Symptom Tracking Chatbots

Here are other advanced healthcare chatbots that are making disease detection functions seamlessly. The conversational bots are designed and developed to analyze the symptoms and recommend a proper diagnosis for patients on booking time slots for the required specialists.

These type of chatbots have shown their potential during the COVID season. AI apps with real-time tracking of self-reported symptoms features have assisted many people in predicting the probable infection and saved their lives from hazardous viral diseases.

  1. Automating Front-Desk or Back-Office Tasks

On the other hand, chatbot applications in healthcare are used for automating front-desk and back-office support functions. OP data management, payments management, and invoice management functions are automated by deploying AI-powered medical & healthcare chatbot applications. It will lower operational cost and improves business efficiency.

  1. Healthcare Insurance Management

AI and machine learning-based healthcare apps with in-built chatbots play a major role in online insurance claiming and processing functions. Supportive document scanning, verifications, credit edibility checking, processing coverage for a medical procedure, and insurance disbursement & record maintenance, everything can be handled robustly using AI insurance chatbots. Hence, insurance claiming bots will save the time of insurers and healthcare service services and make the process faster.

  1. For Responding To Client’s FAQs

NLP plays a key role here to better analyze the user’s voice or text-based questions. Conversational question-answer type chatbots are the next biggest assets for healthcare service providers.

These types of AI healthcare or medical bots are well-trained with a set of pre-defined questions and answers. So, when a user asks a question from the list, the chatbot gives an automated response in minutes.

  1. Patients’ Feedback Monitoring

Here is one of the best applications for using AI chatbots in the healthcare and medical industry. Patient experience and satisfaction is the growth indicator of a healthcare service company. It can be achieved by using AI-powered intelligent feedback analysis chatbots.

Leveraging emotional tracking tools, AI healthcare chatbots can easily detect the experiences of in-patients and out-patients and derive valuable insights. These insights would help service providers for improving service quality and enrich patients’ experiences.

  1. AI bots For Personal Assistance     

AI virtual assistants in healthcare will deliver post-operative care services. Integrating conversational AI chatbots into the intelligent telemedicine system will help to assess patient conditions and enhance the efficiency of outpatient care services. Such virtual nursing assistants will optimize the postoperative experiences and increase business scalability.

  1. Healthcare Chatbots For Maintaining Data Records

Finally, AI healthcare bots or medical chatbots are also best for better data management. AI-powered data management chatbots will automatically log the entire patient’s data like name, age, and details of physicians, treatment, payment, insurance, etc. Hence, the scope for errors in data is zero.

These are the top 10 applications of AI chatbots in the healthcare and medical industry. The AI-based chatbot applications will deliver incredible benefits to both healthcare service providers and patients.

Your.MD, Sensely, and Ada are a few most popular AI-based medical chatbots used to transform healthcare operational ways and improve the quality of personal healthcare services.

Looking to harness the power of conversational AI in your healthcare business?

Let’s Discuss Your AI Chatbot Development Requirements!

[contact-form-7]

Top Benefits of Medical Chatbots In The Healthcare Industry

Here are a few advantages of AI healthcare chatbots:

  • Healthcare service providers can streamline their regular and back-office support works
  • AI chatbot offers creates a communicative platform and ensures quick response to client queries
  • Conversation or nursing bots make post-operative care services efficient
  • Intelligent online conversations without human intervention save a lot of time and improve productivity
  • AI chatbots play a key role in better engaging patients and improving brand value
  • Physicians can provide instant medical assistance in emergencies through telemedicine services
  • Clinical chatbots can improve patient satisfaction and personalization
  • On deploying AI healthcare bots, business scalability will be improved.
  • Healthcare chatbots will make invoice management and payment processing faster and more efficient.
  • AI healthcare chatbots automate routine tasks and boost employee productivity 

Chatbots In Healthcare: How Much Does It Cost To Develop A Medical Chatbot? 

The cost of AI Chatbots development will depend on its type and functionalities. On average, an AI chatbot application development with basic features will range from $15,000 to $100,000+.

However, the cost of conversational AI solutions is high when you use machine learning, predictive analytics, and NLP-like other revolutionary technologies to ensure robust performance. Using AI-like technologies, our expert mobile app developers build interactive mobility solutions for businesses across various industries.


Let’s hire the best AI Chatbot development company- USM Business Systems.


[contact-form-7]
AI agent governance at scale: from 5 agents to a 500-agent workforce

Governing 5 agents is a review process. Governing 500 agents is an infrastructure problem.

Manual reviews and team-level approvals work when a handful of agents are visible and closely watched. Once agents spread across business units, tools, and environments, that oversight breaks down.

Enterprises need an AI agent governance model that includes centralized identity, reusable policies, and enforcement that holds across the whole agent workforce.

Key takeaways

  • At scale, AI agent governance must move from one-off approvals to centralized controls that hold across every agent, team, and environment.
  • Manual review breaks when agents spread across teams, tools, data sources, and environments.
  • Governing an agent workforce requires centralized agent identity, policy propagation, and cross-environment enforcement.
  • AI agent governance teams need visibility into agents, prompts, tools, Model Context Protocol (MCP) servers, data sources, permissions, and runtime behavior.
  • Enterprises should build AI agent governance controls before agent sprawl reaches production scale.

Why governance changes as the agent workforce grows

A small number of AI agents can be governed through direct review. Teams can document purpose, inspect prompts, approve tool access, monitor usage, and revisit an agent when something changes.

The challenge escalates as the AI agent workforce expands across business units and systems. Consider a healthcare scheduling agent connected to an electronic health record, appointment platform, and patient communications system. One version may be approved to read scheduling data and send reminders. Another may inherit broader access, use an unapproved model, or route protected health information into the wrong workflow. 

Across dozens of agents, a single permission change, tool update, or policy gap can spread before anyone sees it.

The consequences extend far beyond governance operations. A small configuration error can expose sensitive data, disrupt services, trigger an audit, and force expensive remediation across multiple systems. As the agent workforce grows, teams must manage thousands of relationships among agents, tools, data, identities, policies, and environments while keeping controls consistent as the system changes.

Where manual governance breaks first

Governing an agent workforce should begin during design and prototyping, before agents spread across teams and production environments. Retrofitting identity, inventory, policy enforcement, and monitoring after deployment adds cost, disruption, and control gaps.

Where governance breaksWhat happens at enterprise scaleWhat enterprises need
InventoryAgents appear across teams, tools, and environments without a complete record. For example, a governance team may set out to catalog 30 agents and uncover 120 prototypes running in approved platforms, notebooks, internal apps, automation tools, and third-party services.A living registry of every agent, owner, business purpose, deployment environment, and connected component.
IdentityShared credentials, broad service accounts, inherited human access, and agent-to-agent handoffs make it difficult to determine who acted and under what authority.A unique identity for every agent, tied to scoped permissions, approved tools, data access, and business purpose.
Policy consistencyTeams interpret the same rule differently, and controls may apply in one workflow or environment but not another.Central policies that propagate across the agent workforce based on risk, data sensitivity, business purpose, and environment.
Environment driftControls can weaken or disappear as agents move through development, staging, production, cloud, on-premises, or third-party platforms.Cross-environment enforcement that keeps identity, permissions, monitoring, and review requirements intact throughout the lifecycle.

What does governance infrastructure for an agent workforce need to include? 

Governance at the scale of an agent workforce requires infrastructure that manages individual agents and coordinates the system around them. An agent is like a machine on a factory floor: teams still need to inspect it, tune it, replace faulty parts, and verify that it operates safely.

At enterprise scale, maintenance is only part of the job. Teams also need to know how each machine connects to the production line, which inputs it can use, which actions it can take, and how the system responds when conditions change.

For agent systems, that means governing prompts, tools, MCP servers, vector databases, data sets, guardrails, APIs, downstream workflows, and predictive and generative models — including the LLMs that power agent reasoning — through a shared control layer.

Governance areaWhat teams need to control
Agent registryWhich agents exist, who owns them, and where they run
Agent identityHow each agent is authenticated, authorized, and tracked
Policy propagationWhich rules apply across agents, tools, data, and environments
Permission scopeWhat each agent can read, write, update, delete, or trigger
Tool accessWhich tools, APIs, MCP servers, and workflows each agent can invoke
Component lineageWhich prompts, models, data sources, and versions each agent uses
Runtime enforcementWhich actions are blocked, escalated, logged, or allowed
MonitoringWhich behaviors indicate drift, misuse, cost spikes, or policy violations
Audit trailsWhat the agent saw, selected, called, returned, decided, and did
Review triggersWhich changes require reapproval before continued use

This infrastructure gives enterprises a practical way to scale agents without relying on scattered spreadsheets, one-off approvals, or disconnected logs.

Three of these areas are worth unpacking. Agent identity, policy propagation, and cross-environment enforcement are what separate governance that works for one agent from governance that holds up across hundreds of them.

How does centralized agent identity work?

You can’t scope permissions, propagate policy, or attribute actions without first assigning every agent a durable, unique identity. Agent identity gives every agent a durable record and a controlled way to act. That record should connect the agent to its owner, business purpose, risk tier, approved tools, data access, deployment environment, and review history.

For example, a procurement agent may compare vendor quotes and draft a recommendation while remaining blocked from approving purchases or changing supplier records.

Identity also separates user authority from agent authority. A human user may have access to a system, but an agent acting on that user’s behalf should still operate within its own approved scope.

Centralized identity also needs to persist across agent-to-agent workflows. When one agent delegates a task to another, governance teams need to know which agent initiated the handoff, what data and instructions moved with it, and what authority the receiving agent was allowed to exercise. Each agent should enforce its own permissions while the system preserves a trace of the full delegation chain. Otherwise, a routine handoff can unexpectedly expand access, drop an important constraint, or make responsibility difficult to reconstruct.

This distinction becomes critical at enterprise scale. When hundreds of agents act across systems and delegate work to one another, security and governance teams need to attribute behavior to specific agents, detect anomalous access patterns, trace handoffs, and revoke permissions without disrupting unrelated workflows.

What is policy propagation and why does it matter? 

Policy propagation turns governance rules into reusable controls across the agent workforce. A policy might define which data classes an agent can access, which tools require human approval, which actions are prohibited, which logs must be captured, or which environments can run high-risk workflows.

At the scale of an agent workforce, these rules should be applied centrally and inherited by the right agents based on risk tier, business purpose, environment, and data sensitivity. A high-risk HR agent, for example, should inherit stricter review, logging, and bias monitoring requirements than a low-risk internal documentation agent.

Policy propagation also helps teams manage change. If a new regulatory requirement affects agents that process personal data, governance teams should be able to identify impacted agents, update the relevant policy, apply it across environments, and verify enforcement.

Without reusable policy controls, each agent becomes its own governance project. That’s not only exhausting for AI, security, and governance teams; it also creates inconsistent enforcement, missed controls, and real operational risk as the agent workforce grows.

How does cross-environment enforcement reduce production risk?

Cross-environment enforcement ensures that governance controls — identity, approved scope, policy requirements, monitoring rules, and audit expectations — move with an agent across development, staging, and production, as well as across cloud, on-premises, and third-party platforms. 

Agents don’t stay still: they connect to new tools, switch models, receive prompt updates, and expand into new workflows.

This is especially important for enterprises that run agents across multiple clouds, on-premises systems, and third-party platforms. A governance program tied to only one deployment environment leaves gaps wherever agents are built or deployed elsewhere.

Cross-environment enforcement should cover access, tool invocation, parameter constraints, guardrails, logging, escalation, and review triggers. It should also prevent unapproved changes from silently expanding what an agent can do.

What leaders should ask before agent growth outruns the governance model

Informal governance starts to strain as agents spread across teams, environments, and business processes. Before growth outruns the governance model, leaders should confirm that the organization can answer these questions:

  • Do we have a central registry of every agent and connected component?
  • Does each agent have a named owner, business purpose, and risk tier?
  • Does every agent have a unique identity with scoped permissions?
  • Can we enforce reusable policies across teams, environments, and deployment platforms?
  • Can we see which tools, MCP servers, APIs, data sources, and workflows each agent can access?
  • Do we track prompts, models, tools, vector databases, data sets, and retrieval sources as versioned components?
  • Can we detect permission drift, policy violations, retry loops, cost spikes, and anomalous behavior?
  • Can we reconstruct an agent’s decision path, including context, tool calls, parameters, returns, and outcomes?
  • Do prompt, model, tool, workflow, or permission changes trigger reapproval?
  • Can we retire one agent and revoke its access without disrupting the broader agent workforce?

Weak answers signal that agent growth is outpacing the governance model. Strong answers give AI, security, governance, and business teams the control infrastructure required for production scale.

Govern your agent workforce before scale becomes sprawl

Agentic AI can create real business value, but production scale requires more than architecture and deployment. Enterprises need governance mechanics that hold up when agents spread across teams, systems, and environments.

The shift from 5 agents to 500 agents changes the job. Centralized identity, policy propagation, cross-environment enforcement, monitoring, auditability, and lifecycle review become the operating foundation.

These workforce-level controls are one part of the broader agentic AI lifecycle. For a deeper look at governing agents, tools, permissions, monitoring, auditability, and production risk, download The Enterprise Guide to Agentic AI Governance.

FAQ

What is agent workforce governance?

Agent workforce governance, sometimes called AI agent governance, is the practice of managing many AI agents through centralized controls for identity, ownership, permissions, policy enforcement, monitoring, auditability, and lifecycle review.

Why are 5 agents and 500 agents different governance problems?

A small number of agents can often be reviewed manually. Hundreds of agents require infrastructure for centralized identity, reusable policies, cross-environment enforcement, runtime monitoring, and audit trails across the agent workforce. 

When should enterprises start planning for agent workforce governance?

Enterprises should start during design and prototyping, before agents move into broad production use. Manual reviews, scattered inventories, and team-level policy enforcement become harder to sustain as an agent workforce expands across teams and environments.

What should enterprises track for every AI agent?

Enterprises should track owner, business purpose, identity, risk tier, model, prompts, tools, MCP servers, data sources, permissions, deployment environment, monitoring signals, audit logs, and review triggers.

What is the biggest risk of an unmanaged agent workforce?

The biggest risk is uncontrolled agent sprawl. Agents may gain unauthorized access, operate under inconsistent policies, drift after system changes, or take actions that teams cannot reconstruct after an incident. 

The post AI agent governance at scale: from 5 agents to a 500-agent workforce appeared first on DataRobot.

A flapping robot swims and flies like a diving bird

Image copyright: Raphael Zufferey.

By Jennifer Chu

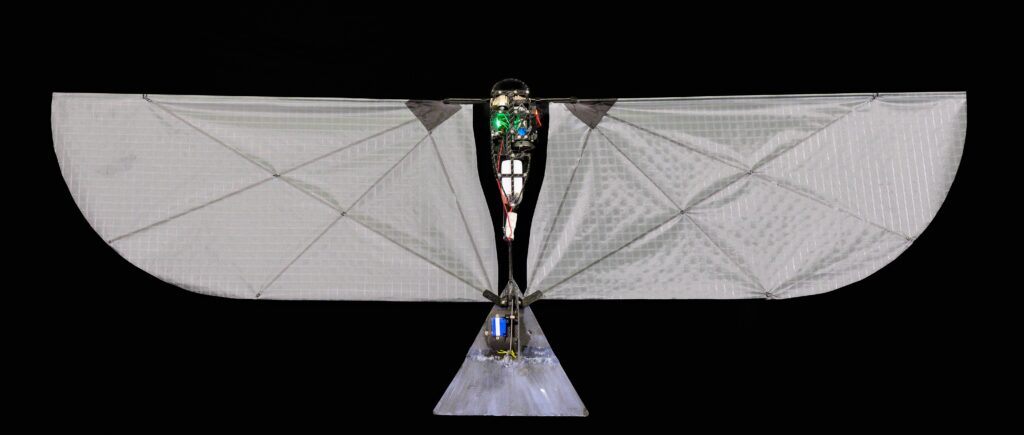
Loons, gulls, puffins, and petrels are some of the 100 species of birds that can both fly and swim. These diving birds can plunge in water to swim after prey, and then leap back into the air to fly away. Now, inspired by these naturally aquatic aviators, engineers at EPFL and MIT have designed a robot that can swim underwater, and flap out of the water to continue flying through air, much like diving birds.

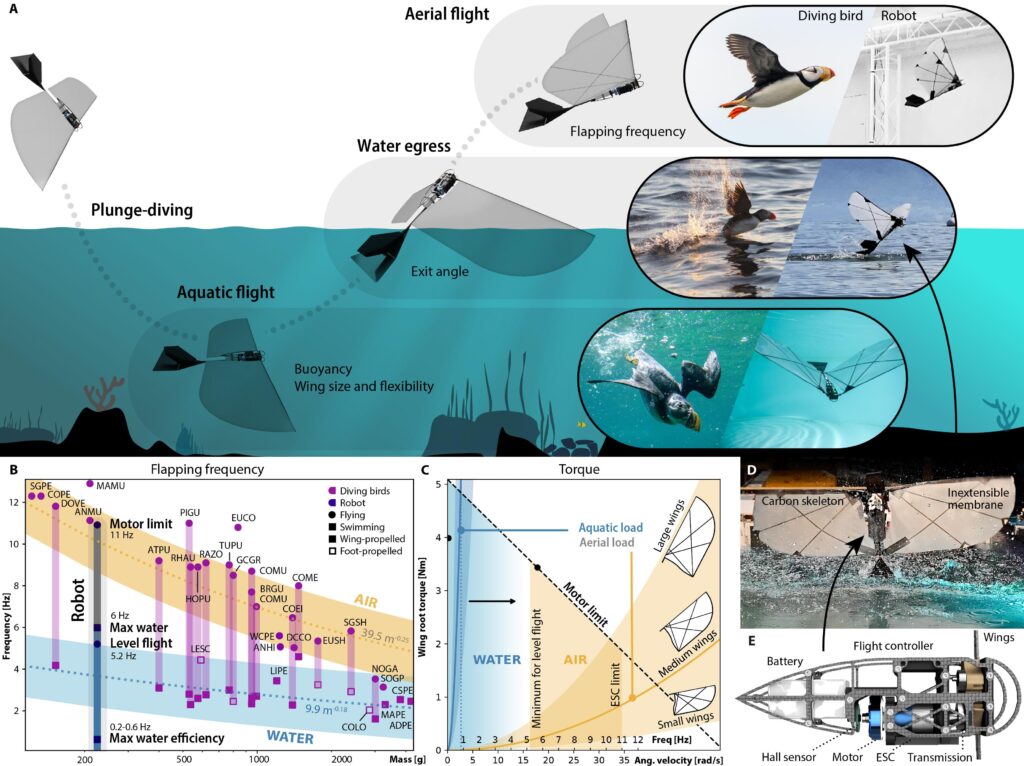
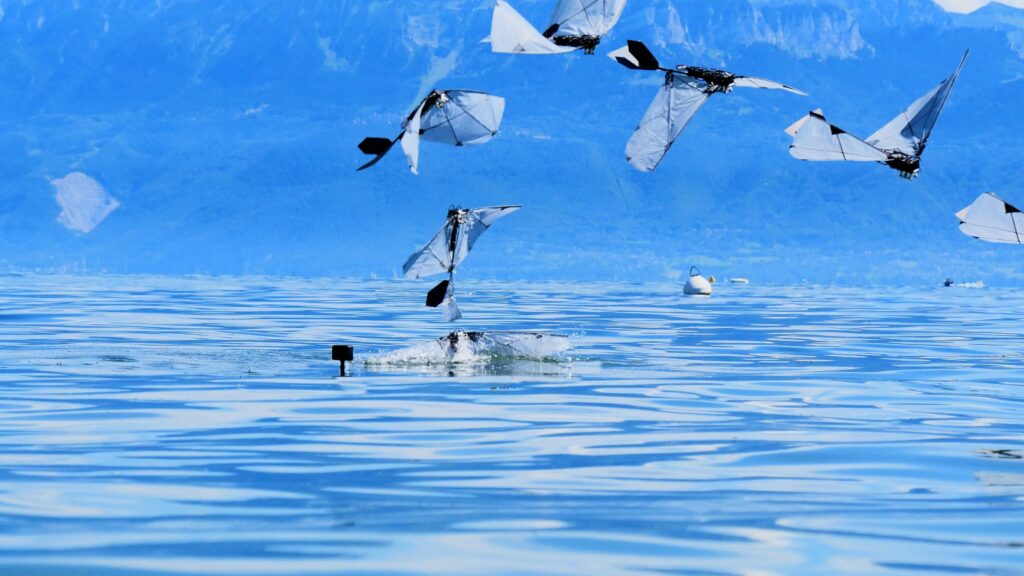
The “flapping-wing aerial-aquatic vehicle,” or FAAV, weighs less than 300 grams and is designed to help scientists study the mechanics that enable diving birds to fly through air and water. The robot has a central body, or fuselage, two flexible, flapping wings, and a steerable tail. The wings and tail can be swapped out for different sizes. In experiments carried out in a water tank and a lake, the engineers identified combinations of wing size, flapping frequency, and tail angle that enable the robot to smoothly transition from swimming through water, to breaking through the surface, to flying through the air.

Their results, published in Science, can help scientists understand how diving birds adapt their flight mechanics to move through air and water, which have very different physical properties. The design could also launch a new class of aerial-aquatic drones and vehicles. The researchers envision such winged robots could be deployed to fly to and sample from aquatic regions that would otherwise be too dangerous for traditional ocean vessels to access.

Image copyright: Raphael Zufferey.

“Our dream vision is for oceanographers, marine biologists and coastal communities to launch this robot from a boat, or from shore, and it would fly close to the area of interest, such as an iceberg, a port facility or over a pod of whales,” says lead author and former EPFL researcher Raphael Zufferey, now an assistant professor of mechanical engineering at MIT. “It would dive into the water to take a measurement or collect a sample, and fly back to deliver the data at a fraction of the cost of traditional methods. Then it could go back out to dive for more.”

Flight mechanics

Zufferey began working on the robot as a postdoctoral fellow in the Laboratory of Intelligent Systems (LIS) and Biorobotics Lab (BioRob) in EPFL’s School of Engineering, under the supervision of respective lab heads and co-authors Dario Floreano and Auke Ijspeert. He completed the work at MIT, where he now leads the AURA Lab, which focuses on engineering bioinspired aerial and aquatic vehicles. The study also includes co-authors from Northwest Indian College (USA).

With bird biomechanics in mind, the team developed a robot with wings made of thin membranes coated with hydrophobic nanoparticles to help wick away water. The body contains a battery and a waterproof electric motor that drives a crankshaft, which in turn pumps the wings up and down at pre-set frequencies. The tail is motorized, enabling it to change its angle to help the robot fly up or dive down.

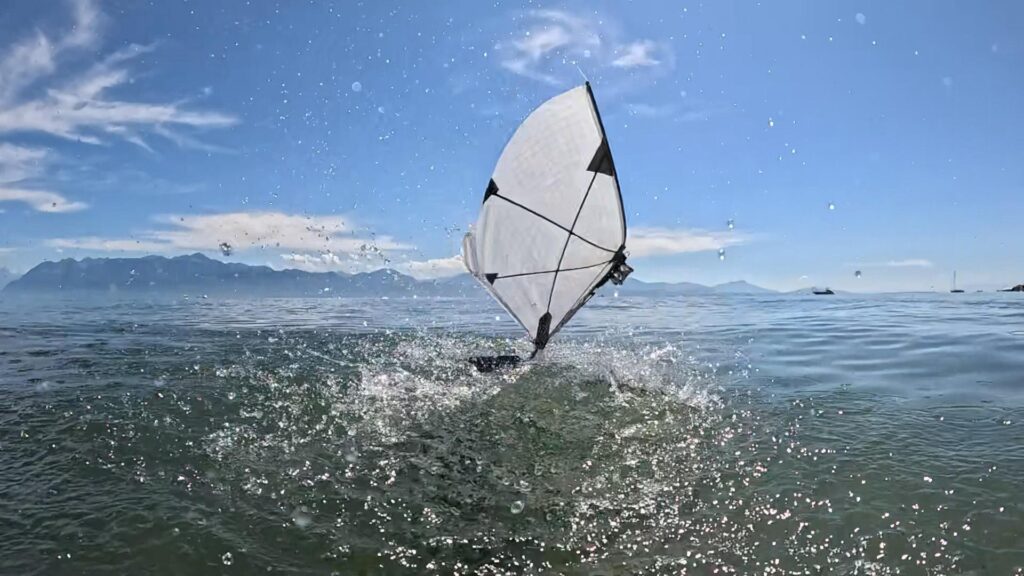
The researchers performed experiments first in a small water tank at EPFL, and then in Lake Geneva. They found that wing size (80 centimeters) and flexibility are key; the wings need to be flexible enough to minimize flapping amplitude in water, and firm enough to keep the robot aloft in the air. The robot could swim at speeds of almost one meter per second when it flapped with a frequency of around 5 hertz (five flaps per second), and fly at around 6 meters per second when flapping at a similar frequency. These speeds and flapping frequencies are similar to those of actual diving birds. To make the leap from water to air, the robot must be pitched at a relatively steep 70 degrees to keep its wingtips from touching the water’s surface.

Image copyright: Raphael Zufferey.

Like a bird, but without feet

Interestingly, this combination of wing size, flap frequency, and tail pitch enabled the robot to swim underwater, launch off the surface, and fly without something that many diving birds require: feet. “If you look at birds, most birds need to paddle their feet at the surface to take off. And the question was, do we need the same for robots? And it turns out we don’t,” Zufferey says. “No one’s been able to fly out of the water with wings.”

Going forward, the team is improving the design of the wings to enable them to turn in addition to flapping up and down. They will also test the robot’s performance under turbulent conditions, such as swimming out of choppy waters, and flying through wind. Then, they hope to deploy the vehicle to help answer questions in ocean science.

Reference

Leaping out of the water: Aerial-aquatic locomotion with flapping wings, Raphael Zufferey, Simon L. Jeger, Moritz Hüsser, Fernando Ruiz, Anthony Lapsansky, Auke Ijspeert, Dario Floreano, Science (2026).

What a first-class agent identity actually is, and whether it is just workload identity

What a first-class agent identity actually is, and whether it is just workload identity

The previous post left you with a borrowed credential and a non-deterministic actor that a static grant cannot govern. The fix is to stop borrowing. Give the agent a stable, verifiable runtime principal you can authorize against, attribute actions to, and revoke on its own.

That sentence hides four requirements. Pull them apart.

The four things an agent identity needs

A first-class agent identity has four parts: a distinct principal, scoped permissions, a clear owner, and an independent kill switch.
Figure 1. A first-class agent identity has four parts: a distinct principal, scoped permissions, a clear owner, and an independent kill switch.

A distinct principal. The agent is its own actor, not a human it impersonates and not a shared service account it hides inside. Its actions resolve to it.

Scoped permissions. The grant is narrower than any human’s, sized to the task, not to the person who launched it. Scope is the answer to the non-determinism problem from Part 1: you cannot predict every action, so you bound the space the agent can act in.

A clear owner. Every agent traces back to a person or team accountable for it. An identity with no owner is a liability with no name on it.

A kill switch. You can revoke the agent without touching anyone else’s credentials. Independent revocation is what makes the identity safe to hand out in the first place.

Miss any one of these and you are back in Part 1. The alternatives engineers reach for first each miss at least one.

ApproachActor modelAttributionScopingRevocationWhere it breaks
Shared service accountOne identity, many agentsNone: all agents look identicalCoarse, shared by allRevoke one, you revoke allNo way to tell agents apart or shut one off
Per-user impersonationAgent borrows a humanLogs show the human, not the agentInherits the human’s full accessRotating the key breaks the humanThe Part 1 problem, by another name
Static secretA long-lived keyTied to a secret, not an actorWhatever the secret was minted forNo rotation, no clean revocationSecret leaks, lives forever, scopes nothing
First-class agent identityA distinct principalActions resolve to the agentTask-scoped, narrower than a humanIndependent kill switchCost of running it as real infrastructure

Table 1. The same four questions, asked of every option people try before they give the agent its own identity.

The question a good engineer is already asking

If the agent gets a stable runtime principal with scoped permissions and a kill switch, you have described workload identity. So is agent identity just workload identity with a new label?

This is a live debate, not a settled point, and the honest answer is: it depends. It depends on three invariants.

When the three invariants hold, agent identity collapses into workload identity. When they break, it becomes a layer on top.
Figure 2. When the three invariants hold, agent identity collapses into workload identity. When they break, it becomes a layer on top.

A one-to-one mapping. One agent corresponds to exactly one workload. When that holds, the workload’s identity is the agent’s identity.

A registry as the source of truth. Something authoritative records which agents exist and what they are. Without it, you cannot reason about the population of agents, only about individual processes.

Identity continuity. The identity survives restarts, pauses, and reschedules. The agent that comes back up is provably the same agent that went down.

When all three hold, agent identity collapses into workload identity. You attest the workload with something like SPIFFE or WIMSE and you authorize against it directly. No extra layer earns its place.

When they break, agent identity becomes a layer on top of workload identity. And they break often. Agents are bursty. They are ephemeral. They churn across workloads instead of pinning to one. They spawn sub-agents that have no workload of their own to attest. The one-to-one mapping dissolves, continuity gets hard, and the workload is no longer a faithful stand-in for the agent.

What the shipping platforms tell you

The publicly announced platforms show the layered pattern in production. Microsoft Entra Agent ID introduces a specialized principal that extends an existing directory, rather than reusing a plain workload identity. AWS Bedrock AgentCore exposes a stable agent identity that sits above a sandboxed workload, which can churn underneath without the agent’s identity churning with it.

Notice what both share. Each lives inside a single control plane and a single trust domain. One system issues the identity, governs it, and can see every hop the agent makes, because every hop happens on home turf. That is what makes the layered model tractable for these platforms.

Hold that observation. It is doing more work than it looks like, and it is the assumption that breaks in Part 4.

The take-away

An agent identity is a stable runtime principal with its own scoped permissions, a clear owner, and an off switch. Whether that is plain workload identity or a layer above it is not a matter of taste. It depends on whether you can hold the one-to-one mapping, a registry as source of truth, and continuity across the agent’s life. Audit your own agents against those three invariants. Where they break is where you need the extra layer, and where most real fleets live.

You now have a single agent with an identity. Real systems are not single agents. A user calls an agent, the agent calls a tool, the tool calls another agent, and the identity has to survive every hop. The next post is about what happens to identity in that chain, and the protocols that either preserve it or destroy it.

The post What a first-class agent identity actually is, and whether it is just workload identity appeared first on DataRobot.

AI agents create virtual playgrounds to help robots get crucial training data

Robots walking down the street, surrounded by astounded onlookers, are an increasingly common sight. But these machines aren't yet the do-it-all assistants you'd want working in a kitchen or factory, and a major bottleneck is data. Much like humans, robots learn best by experience. The challenge is that it's labor-intensive and time-consuming to physically teach these machines so many actions across different settings.

Alan Turing’s biggest AI assumption may have been wrong

A new book claims AI has been built on a flawed assumption dating back to Alan Turing's famous 1950 paper. Peter J. Denning argues that the most important parts of human intelligence, including common sense, intuition, culture, and practical know-how, cannot be encoded into computers. He believes this makes true human-level AI impossible, regardless of how large language models become.

Predictive Analytics in Logistics: Applications & Use Cases

Predictive Analytics in Logistics: Applications & Use Cases

Predictive Analytics in Supply Chain Explained for Logistics Decision Makers

The cost-cutting logistics model worked in the past, but in today’s uncertain business world, it’s no longer enough. Higher operational costs, worldwide supply chain disruption, and customers’ demand for faster delivery are convincing logistics decision-makers to look for advanced alternatives.

This is where supply chain predictive analytics optimizes the way. Data, Machine Learning (ML), and Artificial Intelligence (AI) come together to provide decision-makers with a sense of what’s going to occur in the future, transforming the way they can make informed, competitive decisions. Let us look at what predictive analytics actually do for supply chain and logistics operations.

What Predictive Analytics Really Means for Supply Chain Operations?

Predictive analytics supply chain informs companies about the outcome of tomorrow. Leveraging the past history, customer preferences, market trends, and even external determinants like fuel prices or weather conditions, predictive solutions can foresee the peak demands, slowdowns, or market risks.

To decision-makers in logistics, it means breaking free of reaction firefighting and forward-looking planning. Rather than holding back until something fails, leaders can get ahead of it and take ownership of what tomorrow will look like. 

Why Predictive Analytics Matters for Logistics Decision Makers?

In logistics, one disruption can cascade through the supply chain and increase costs and destroy customer relationships. Predictive analytics indicates that leaders improve demand forecasting, inventory, and exposures by supplier performance. It also enables better transportation planning with the capacity to forecast fuel changes and traffic congestion in the future.

Research indicates that the companies adopting predictive analytics for logistics realize fifteen percent lower inventory cost and 20% lower delivery time. Predictive analytics not only saves organizations costs; it’s driving business performance. 

Top Use Cases of Predictive Analytics in Supply Chain Management

  • Demand Forecasting: Anticipating Customer Needs

At the heart of predictive analytics lies demand forecasting, the ability to anticipate what customers will want, when they will want it, and in what quantity. Based on past sales, seasonality, and market trends, supply chain companies can schedule manufacture, procurement, and shipping to actual demand using predictive analytics solutions.

This reduces both overstock and shortages, creating a leaner, more responsive supply chain. This ensures that the decision-makers are no longer to rely on guesswork, but rather they can operate with accuracy and confidence. When you can predict demand, you can predict growth.

  • Route Optimization: Delivering Smarter and Faster

Transportation is perhaps the most significant cost factor in logistics and is made even trickier with uncertainty added to the mix. By analyzing real-time traffic, weather, and fuel costs data, predictive analytics solutions turn the process and suggest the best routes of delivery.

This will have products moving at maximum efficiency and lower cost, improving consumers’ experiences while cutting costs. Predictive route optimization managing leaders do not only imagine costs going down but also imagine higher reliability. 

Recommended To Read: How is AI Revolutionizing Supply Chain and Logistics? 

  • Supplier Risk Management: Strengthening the Weakest Link

A supply chain is only as strong as its weakest supplier, and disruptions can cause massive setbacks. Predictive analytics gives logistics leaders the ability to examine supplier performance, financial health, and even geopolitical risk in hopes of discovering weaknesses before they damage their business.

By anticipating this beforehand, planners can select standby suppliers, reschedule contracts, or design standby plans beforehand. Instead of being reactive to bad failures, supply chain managers are able to provide uninterrupted service.

  • Inventory Optimization: Balancing Cost and Availability

Managing inventory is one of the toughest challenges in logistics. Excess inventory ties up capital and raises storage costs, while insufficient inventory risks customer dissatisfaction and lost revenue.

Predictive analytics avoids the dilemma by anticipating product movement and stocking in advance. It keeps bestsellers in stock and flops not worth stocking. It means better margins and healthier balance sheets for decision-makers. The wisest supply chains are lean, agile, and analytics-based.

  • Customer Insights: Staying Ahead of Expectations

Logistics is no longer just about moving goods; it’s about understanding customers. Predictive analytics gives companies precise information regarding preference, buying habits, and seasonality so that companies can even make an educated estimation of their needs before the customers themselves can articulate such needs.

This kind of personalization creates greater loyalty and makes companies more prominent in a noisy marketplace. Companies can develop customer-centric programs that gain long-term success. Therefore, with AI and predictive analytics in place, organizations can better understand their customers and their preferences. 

Recommended To Read: AI in Supply Chain: Top Use Cases of AI in Supply Chain Management

The Future of Predictive Analytics in Logistics

The future is for those who prepare and jump into predictive analytics already. More than half of all supply chains globally will utilize advanced analytics by 2027, according to a Gartner estimate. Also, according to Statista, the predictive analytics software market is anticipated to grow to more than $41 billion by 2028.

Predictive analytics isn’t going away for supply chain decision-makers, it’s the key to victory. The first movers are the ones with the velocity, flexibility, and customer loyalty to capture market share, and followers will be in their dust. The future has arrived, and predictive analytics are at its forefront.

The Cost of Supply Chain Management App with Predictive Analytics

Building a predictive insight supply chain management application would be as much a growth initiative as it would be an information technology undertaking. Costs of AI mobile app development will depend on how sophisticated the application is, the feature set, integrations, AI/ML features, and the size of your logistics company.

Companies would expect to pay $60,000 to $150,000 for a tailored AI solution.

A basic predictive app with features like order tracking, inventory management, and real-time dashboards will fall on the lower end of the spectrum. However, when predictive analytics is added, covering demand forecasting, route optimization, supplier risk modeling, and advanced data visualization, the investment rises but delivers significantly higher ROI.

In fact, companies leveraging AI-enabled supply chain software have a maximum of 30% lower operation expense and 20% to 25% improved delivery performance. However, it’s not about how much it costs to build a predictive analytics app, it’s about how much it can save your business.


Recommended To Read: How Much does Logistics App Development Cost? 

USM’s Success Story

A Texas manufacturing firm contracted USM to develop a next-generation and intelligent solution for logistics and supply chain management that utilizes the supply chain operation efficiencies and workload of the supply chain operations to their utmost.

Key Challenges in Building the Predictive Supply Chain App

The two were real-time warehouse monitoring and error-free warehouses. The other was end-to-end supply chain visibility, inclusive of error-free delivery network integration, warehouses, and logistics.

Delivery and shipping notices to the precise location needed streamlined coordination of fleet data and customer dashboards. With all this in the background, we had to develop a secured login portal for customers with new order support as well as pipeline improvement sales.

Our Solution: Turning Vision into Reality

After a detailed analysis of client requirements, our talented mobile app developers crafted a custom supply chain and logistics app for business needs. From development to deployment, each part of the app was honed to perfection to enable it to be scalable, precise, and real-time driven.

We employed the most recent frameworks, AI-driven tracking, and deep integration to link fleets, warehouses, and delivery networks to one another. We drove intelligence to action by embedding abilities that not only notify but also predict demand and make decisions with little human intervention.

The result? Our AI-driven supply chain platform simplified and surprised the user with real-time tracking, optimized deliveries, and many more incredible benefits. Click here to know more about the AI solution we delivered.

Conclusion

Predictive supply chain analytics is not data, it’s empowering logistics decision-makers to move forward in forecasting, planning, and succeeding. From accurate demand forecasting to smarter routing optimization, it converts uncertainty into opportunity. The future of logistics is in the hands of early adopters who are leveraging predictive analytics.

Contact us to know more about Predictive analytics in supply chain? Book Executive AI Briefing →


Are you ready to lead the way? Let’s talk with our AI experts, today!

[contact-form-7]

Scientists discovered the brain doesn’t make decisions the way we thought

A new study suggests the brain begins making decisions much earlier than scientists previously thought. Researchers found that even primary sensory regions are influenced by higher brain areas through rapid feedback loops, rather than simply passing information forward. This more dynamic view of brain function could help engineers design future AI systems that think more like biological brains while using far less power.
Page 5 of 8
1 3 4 5 6 7 8