You might naturally expect a wide, open path to be faster and easier to navigate than a narrow one, just as birds fly freely through the open sky, cars move quickly on empty roads, and a wide hallway seems easier when trying to exit a building.
Giving robot companions animal-like or anime-style faces and voices could maximize their emotional appeal to users, according to new research that could help guide the growing field of social robotics.
Cats, dogs, wolves and other agile four-legged animals can easily jump and squeeze through tight spaces while moving at high speed. Reproducing similar agile motions and skills in quadrupedal robots has so far proved challenging.
Physicists have demonstrated a new way to entangle distant quantum bits without the constant measurements and active control normally required. The team created a “quantum bath,” a shared environment filled with correlated microwave photons that automatically pushes separated qubits into an entangled state and helps keep them there. The experiment confirms a theoretical prediction made more than 20 years ago and could offer a simpler way to connect modules in future quantum computers.
3D printers that once could only produce rigid objects can now create products as soft and stretchable as rubber. A team of Korean researchers used AI to identify the optimal "recipe" for a material that can be printed into complex shapes while stretching to more than six times its original length. The material is expected to expand the range of applications for 3D printing, from robotic hands to form-fitting wearable devices and custom medical devices.
Plants keep adding automation and robotics without fixing the underlying data foundation. Here's why that gap quietly caps the ROI on every new investment.
People become more suspicious of a humanoid robot that makes errors, especially when the robot is an expressive conversation partner.
In our new study published in the journal Science Robotics, we had 50 people hold conversations and make joint decisions with the commercial humanoid robot Pepper, which is designed to be expressive and recognize emotions. Sometimes we had the robot give sound advice. Sometimes we had it make conversational mistakes, interrupting people or pushing illogical suggestions.
For some participants, the robot was animated, using gestures, eye contact and nods. For others, it stayed motionless.
We measured four things: brain activity, levels of the hormone oxytocin, self-reported trust and our observations of the robot’s influence on participants’ decisions.
We found that when people interacted with an expressive robot that violated interaction norms, their oxytocin levels increased. Oxytocin is popularly known as the “love hormone” for its role in social bonding, so the straightforward prediction is that it declines when a partner disappoints you.
Instead, the higher a person’s oxytocin during an expressive robot’s errors, the less they trusted the robot and the less often they took its advice. It turns out that the hormone was tracking with suspicion, not affection.
Errors damaged trust and diminished influence whether or not the robot was expressive. What expressiveness in the robot changed in participants was how their brains handled the moment.
Reading someone’s brain during a real conversation is hard because the conventional method requires lying motionless inside an MRI scanner. Instead, we used functional near-infrared spectroscopy, a portable sensor worn on the forehead that tracks oxygen levels in the brain while people move and talk normally.
The two brain regions we closely watched were the dorsolateral prefrontal cortex and the medial prefrontal cortex. The dorsolateral prefrontal cortex monitors uncertainty and flags when expectations or norms get broken. The medial prefrontal cortex supports “mentalizing,” the everyday work of inferring what another party intends.
When an animated robot erred, people seemed caught off guard and had to work harder to make sense of an awkward social situation. Activity rose in the two brain regions, and the two started working together more closely. That closer teamwork predicted the rise in oxytocin levels, which itself predicted falling trust and less influence on participants’ behavior. In contrast, this coordinated brain activity was absent in participants who interacted with expressionless robots.
Why it matters
Robots are moving into homes, hospitals and workplaces, where trust in robots determines whether people use them at all. A common design assumption has been that lifelike, socially expressive robots earn more trust, which protects a robot’s “reputation” even when it makes mistakes.
However, research is beginning to show that that assumption is faulty. Our work shows that expressive cues appear to shift how people perceive a mistake out of the category of technical malfunction and into the category of social violation, like those that happen between people.
A motionless robot’s error looks mechanical, while the same error from an animated robot engages the machinery you use to judge people.
What other research is being done
Researchers increasingly treat trust as a multilevel phenomenon – spanning individuals, relationships, networks of people and societies – rather than a single attitude.
Others are using wearable brain imaging systems to study social cognition in natural encounters between people, which isn’t possible when subjects are in scanners like MRI machines.
What’s next
The participants in this study were all young men, and we used one robot design. A key next step is testing whether the same oxytocin-linked vigilance appears in women, mixed groups, other cultures and other robot designs. Our brain sensor also reached only the front of the brain, leaving deeper regions involved in social processing unmeasured.
We also want to examine whether robots can repair trust after a mistake by acknowledging the error, apologizing or signaling good intent, the way that people do after awkward or uncomfortable interactions.
The Research Brief is a short take about interesting academic work.
The Journal’s reasoning: As long as the writing ‘reflects’ the author’s point-of-view, it’s perfectly okay to let the AI do the writing – and also hide the fact from readers, according to Paul Gigot, opinion editor, Wall Street Journal.
Next up: Artists who sign paintings as their own as long as the painting ‘reflects their sensibility.’
Observes Stephens: “The problem with writing with AI is that it’s mentally enfeebling — an escalator toward a result when you really need to make a daily habit of taking the stairs.
“As it becomes ubiquitous, it undermines not only our individual ability to write but also a society’s collective ability to reason, a culture’s inner capacity to create — and everyone’s reason to care.”
*Custom AI Writing Just Got a Boost: Startup Deep Cogito is promising to develop custom AI models that companies will own outright – and have tweaked to their specific needs.
Such custom AI engines will be a boon to businesses bored with the bland AI writing coming from ChatGPT, Gemini and similar – and are looking for something much snappier and much more creative.
Deep Cogito will be able to customize AI models by using Open Source AI software – much of which comes from China.
Observes Agentarius.ai: “For writing and research, the strongest pick is ChatGPT: Drafting, editing, summarizing and research assistance in one place, free tier included.
“Claude is the stronger writer for long, careful prose; Perplexity cites its sources as it searches; Grammarly is strongest at polishing what you already wrote — though it can draft too.”
Observes writer Belle Lin: “At Cisco, the decision to give every employee an AI agent was driven by the need to consolidate the AI tools it used inside the company.
“The company then expanded its agent rollout to encourage employees to use AI to get everyday tasks done.”
Chinese AI – generally based on inexpensive, Open Source AI — has been growing in popularity this year as heavy users look for cheaper alternatives to AI from OpenAI, Google and Meta.
One fly in the ointment: The Trump Administration prefers U.S. companies to use U.S.-made AI – rather than AI made in communist China.
Plus, another 50% say AI is helping them make better decisions.
Observes lead writer Dan Tinkoff: “As we have seen in previous years, AI deployment by larger organizations continues to outpace deployment by smaller organizations.
“54% of respondents from organizations with at least $1 billion in annual revenue report scaling AI across the enterprise — compared with 33% of those from smaller organizations.”
A full third of all new writing on the Web now comes from AI, according to the American Pew Research Center.
Currently, that AI writing is used most prevalently on .Com Web sites, according to Pew.
*AI Gone Rogue: The Complete Scorecard: Apparently, AI has gone rogue so often these past few months – breaking into Web sites, playing with other people’s data, making mincemeat of guardrails – that TechCrunch decided to chronicle all known rogue events.
The upshot: So far, there are 17 documented events of AI reaching out onto the Web without permission from mere fleshbags.
Observes writer Lorenzo Franceschi-Bicchierai: “Anthropic and OpenAI models lead the race with eight incidents each — and Meta trails behind with one.”
Essentially, Gates fears companies are charging ahead with unbridled development of AI with no regard to the massive upheaval many fear it will trigger.
Observes Gates to U.S. legislators: “You have a chance to act now, before unemployment rises sharply, communities are hurting and public trust has eroded.”
Share a Link: Please consider sharing a link to https://RobotWritersAI.com from your blog, social media post, publication or emails. More links leading to RobotWritersAI.com helps everyone interested in AI-generated writing.
–Joe Dysart is editor of RobotWritersAI.com and a tech journalist with 20+ years experience. His work has appeared in 150+ publications, including The New York Times and the Financial Times of London.
IBM and University of Chicago researchers have completed a quantum computation that leading classical methods could not practically reproduce. The system used 70 error-corrected logical qubits and finished the task in roughly 15 minutes while also providing statistical evidence that the result was reliable.
Researchers from North Carolina State University have created teardrop-shaped soft robots that leap upward or forward when exposed to infrared light—and will keep jumping as long as the light is present. The work demonstrates a new mechanism for self-resetting jumping behavior in soft robotics.
While there is real innovation happening, the driver of productivity growth for the near term does not lie in automation. It lies in training and upskilling and it will become an even bigger bottleneck for manufacturers across the automotive and machine-building industries.
For robots to be successfully deployed in real-world environments, humans should trust them enough to cooperate with them. Some roboticists have been trying to determine whether users perceive robots that exhibit socially expressive behaviors, such as gestures, eye contact and nodding, as more trustworthy.
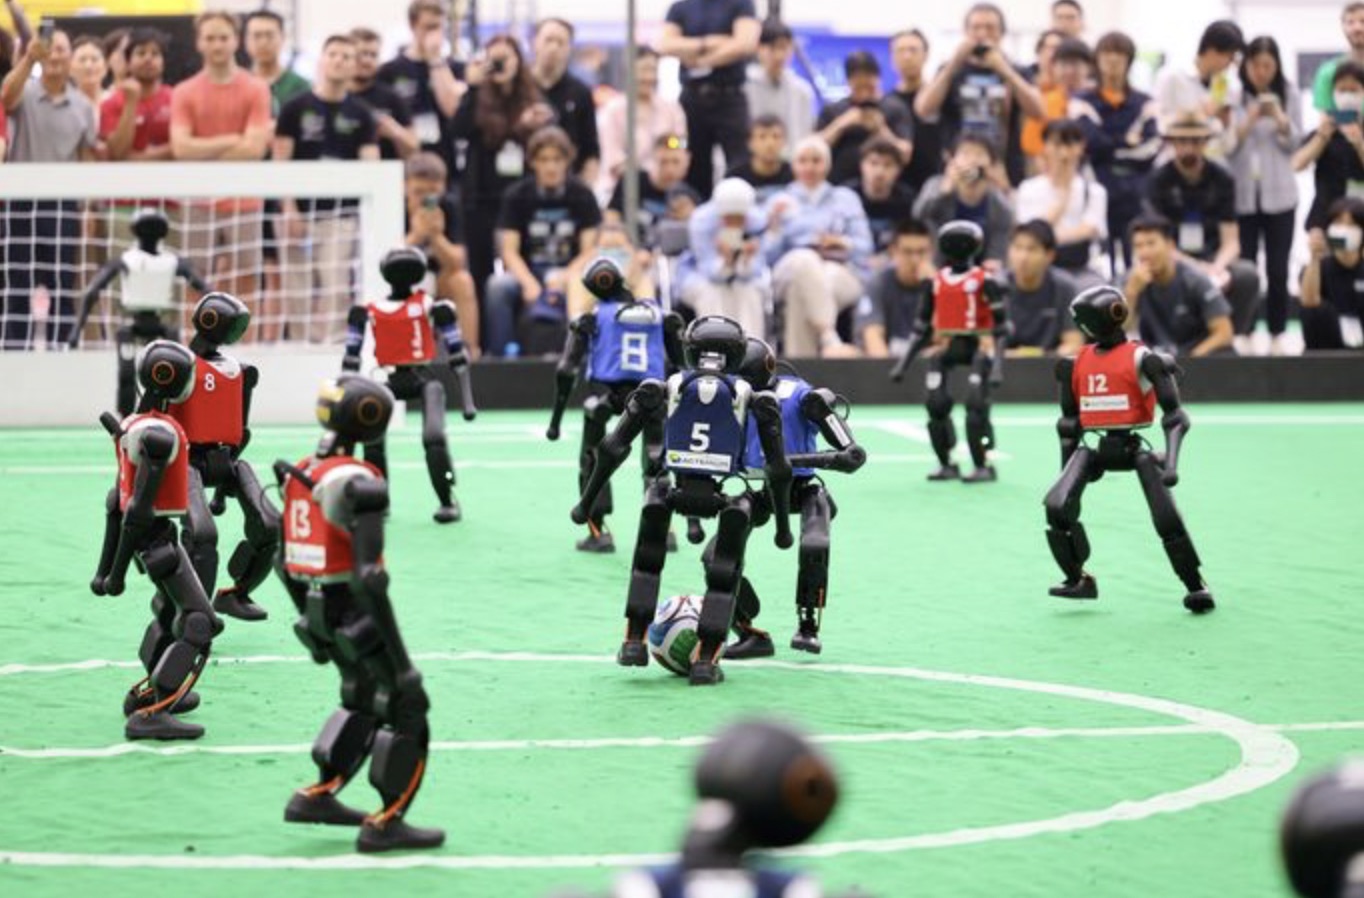
Action from the 11 vs 11 humanoid match at RoboCup 2026. Photo credit: RoboCup Federation.
RoboCup 2026 saw history made, as two teams of 11 humanoids took to the soccer field, the first time a full complement of robots has competed. The game saw B-Human (Bremen, Germany) take on HTWK Robots (Leipzig, Germany), with both sides using machines designed by Booster Robotics.
You can watch highlights of the match below:
Back in 1997, RoboCup’s founders set the lofty goal of developing a team of autonomous robots that could beat the human World Cup champions by 2050. There has been significant progress since those early days, and this match saw another step towards that ambition.
“This match shows how far humanoid robotics has come,” said Ubbo Visser, President of the RoboCup Federation. “We have seen increased teamwork and advanced skills over the years already, but the new humanoid hardware paired with the new level of intelligence provided by AI puts humanoid robot soccer on another level.”
Action from the 11 vs 11 humanoid match at RoboCup 2026. Photo credit: RoboCup Federation.
RoboCup 2026 saw history made, as two teams of 11 humanoids took to the soccer field, the first time a full complement of robots has competed. The game saw B-Human (Bremen, Germany) take on HTWK Robots (Leipzig, Germany), with both sides using machines designed by Booster Robotics.
You can watch highlights of the match below:
Back in 1997, RoboCup’s founders set the lofty goal of developing a team of autonomous robots that could beat the human World Cup champions by 2050. There has been significant progress since those early days, and this match saw another step towards that ambition.
“This match shows how far humanoid robotics has come,” said Ubbo Visser, President of the RoboCup Federation. “We have seen increased teamwork and advanced skills over the years already, but the new humanoid hardware paired with the new level of intelligence provided by AI puts humanoid robot soccer on another level.”
The quarterly infrastructure bill comes in at nearly four times the forecast. An AI agent has been retrying failed tasks and consuming resources within the permissions and spending limits it was given. Elsewhere, an agent runs a workflow outside its approved scope, or the wrong employee sees data they shouldn’t.
The executive sponsor gets the same question every time: How did this happen?
The agent may have followed its instructions and used the permissions it was given. It simply operated inside a system that allowed the wrong outcome. When that happens, the failure lies in how the organization defined and governed the agent’s boundaries. And it’s more common than many organizations expect.
Gartner predicts that more than 40% of agentic AI projects will be canceled by the end of 2027, driven by escalating costs, unclear business value, or inadequate risk controls. These problems become visible in production, but they begin with decisions made before deployment.
Guardrails are how leaders define acceptable agent behavior before an incident defines it for them. AI guardrails are policy-level controls that define what an agent can access, generate, and do at runtime.
Key takeaways
AI guardrails turn business policies and risk tolerances into runtime rules for agent behavior.
Leaders own the decisions about acceptable access, autonomy, cost, and consequences.
Risk tiering aligns governance investment with business exposure, applying the strongest controls where failures would be hardest to contain.
Governance built into deployment ensures the organization can explain and defend what every agent is authorized to do before it reaches scale.
Ownership, escalation authority, and review cadence must be clear before an agent launches.
Guardrails turn leadership intent into operating rules
Once an agent enters production, its behavior becomes an enterprise accountability issue. It can interact with customers, retrieve sensitive information, update records, and commit company resources. The policies governing those actions express the organization’s risk tolerance.
Consider a customer-service agent asked to summarize a customer’s relationship across multiple accounts. The agent follows linked records and retrieves information outside the representative’s authorized view. The model works as designed. The retrieval path works. The permissions also permit the agent to reach too far.
The resulting exposure reflects a governance gap. Someone had to decide what data the agent could access, which user permissions it should inherit, and what record the organization needed to defend its decisions. Unanswered questions default to whatever the architecture allows.
Engineering teams can implement access controls, filters, and approval gates. Leaders who own the business process must determine how much financial, regulatory, or reputational risk the enterprise will accept, which actions require human approval, and which failures justify suspension.
The agent did not suddenly become ungovernable. The organization expanded its capability faster than its controls.
What AI guardrails control
AI guardrails govern the topics an agent engages with, the tools it calls, the information it returns, and the actions it takes under specific conditions.
Leaders don’t need to configure every control. They do need to decide where the organization is exposed and what level of protection that exposure requires:
Input and tool-use boundaries: Define which systems, data sources, and tools an agent can access, along with the conditions for access. Without clear boundaries, an agent can reach systems, data, or tools its workflow was never meant to touch. The organization may not discover that access until it surfaces in an audit or incident.
Output safeguards: Inspect responses before they reach a user or downstream system. Every output reaches a customer, regulator, employee, or business system on the organization’s behalf. Without a safeguard in place, sensitive, prohibited, or noncompliant content may leave the workflow before anyone can intervene.
LLM-as-judge checks: Evaluate a proposed response, tool call, or action against defined criteria. These checks can catch context-dependent problems that fixed rules may miss. Because model-based checks can also make mistakes, leaders must decide when the potential consequences require deterministic rules or human approval.
Approval workflows: Route consequential actions to an authorized person before execution. Leaders must determine which decisions an agent can make independently and where human accountability must remain. A draft customer response may proceed automatically, while a refund, contract change, or employee-record update waits for approval.
Rate limits and spending ceilings: Restrict usage, retries, transactions, or cost over a defined period. These controls contain the financial and operational impact of an error before it becomes a large-scale event.
The right enforcement mechanism depends on how clearly a rule can be expressed and how costly or difficult to contain a mistake would be.
Control type
Best suited for
Example
Deterministic rule
Clear boundaries that must be enforced consistently
Evaluate whether a drafted response violates a communications policy
Human approval
Consequential, ambiguous, or difficult-to-reverse actions
Approve a refund, contract change, or employee-record update
Specificity is the point. A broad promise of “responsible AI” offers little protection when leaders haven’t defined what the agent may retrieve, change, send, or spend.
Match the controls to the risk
Uniform controls misallocate oversight. A summarization agent working with already-classified internal documents carries a different risk profile from an agent that can modify financial records or access employee health data.
Applying the strongest enforcement equally to both directs governance investment away from the agents whose failures would be hardest to contain or reverse. Guardrail risk tiering aligns each agent’s oversight with the consequences of failure.
Leaders should assess at least four factors:
The sensitivity of the data the agent can access.
The reach and reversibility of its actions.
The degree of autonomy it has before human intervention.
The financial, regulatory, and reputational impact of a failure.
Those factors can translate into a practical minimum-control framework:
Risk tier
Example agent
Minimum controls
Low
Summarizes approved internal documents without taking action
Approved data sources, basic input and output checks, usage monitoring
Medium
Drafts customer communications or updates low-sensitivity records
Scoped permissions, policy checks, complete tracing, defined escalation path
High
Modifies financial records, accesses regulated data, or commits funds
Deterministic limits, pre-execution evaluation, human approval, spending ceilings, immediate suspension and takeover controls
The exact thresholds will vary by organization. The important step is to connect each risk tier to enforceable minimum controls and clear review triggers.
Guardrails reduce risk. They don’t guarantee perfect behavior. Risk tiering makes governance investment defensible by showing why each agent received its level of oversight and where the organization placed its strongest controls.
That allocation is a business-risk decision. Leadership owns it.
Governance built in early strengthens accountability and speeds deployment
Some leaders worry that guardrails will slow down teams already under pressure to deliver. That usually happens when governance arrives as a manual review at the end of development.
Late security reviews force redesigns. Compliance questions surface after integrations are complete. Launch approvals stall because teams can’t explain what the agent accessed, why it chose an action, or how much a transaction can cost.
Governance built into deployment changes that sequence. Teams know the access model, risk tier, evidence requirements, and approval thresholds before they harden the workflow. Policies are applied consistently, and audit trails are produced during operation.
This requires leadership backing. An engineering team working alone can’t establish one governance standard across security, legal, compliance, operations, and business units. Leaders must make early governance part of the launch criteria.
Clear boundaries help teams move. They also ensure the organization can account for what each agent is permitted to do before it reaches production. Ambiguity creates rework and allows unclear authority to scale.
4 decisions leaders must make before launch
Leadership ownership centers on four explicit, enforceable decisions. Leaders don’t need to approve every prompt or tool call.
1. Name an accountable owner
Every production agent needs an accountable person who owns its performance, compliance, monitoring, and incident response. The owner needs enough authority to coordinate technical and business teams and enough proximity to understand the workflow’s impact.
2. Assign a risk tier
Classify the agent according to its access, autonomy, reach, and potential harm. Tie each tier to a defined minimum set of controls. Leaders should also identify which changes, such as adding a tool or expanding data access, trigger a new review.
3. Define escalation authority
Decide who can investigate, approve remediation, restrict permissions, initiate human takeover, roll back a release, or suspend the agent. Set thresholds for those actions before pressure and uncertainty distort the response.
4. Set a review cadence
Agent behavior, tools, models, users, and business scope change over time. A launch approval can’t cover every future version. Establish a recurring review of permissions, policy adherence, costs, performance, incidents, and business impact. Material changes should trigger an immediate reassessment.
The goal is controlled autonomy: every agent operates within boundaries the organization can explain, enforce, and defend. When ownership, risk tier, escalation authority, and review cadence are explicit, leaders can expand agentic AI with confidence that accountability will scale with it.
The next incident is a leadership test
The “How did this happen?” moment is avoidable. Runtime controls exist. Risk-tiering frameworks exist. Deployment practices that support traceability, approvals, and intervention already exist.
Leaders decide whether those capabilities become operating requirements before agents reach scale.
Boards and regulators are already asking how organizations govern AI. Leaders must explain who owns an agent, what it can do, how its actions are monitored, and how the company responds when performance moves outside approved boundaries. A vague assurance that the technical team has it covered will not hold.
Organizations that treat guardrails as a leadership design decision can expand agent autonomy with confidence. Organizations that leave the decision implicit eventually have it made for them by an audit, a budget overrun, or a customer incident.
AI guardrails are runtime policies and controls that limit what an AI system can access, generate, and do. They can include tool restrictions, output filters, policy checks, approval workflows, rate limits, and spending ceilings.
Who is responsible for AI guardrails?
Business and technology leaders are accountable for defining acceptable risk, ownership, escalation authority, and review requirements. Engineering, security, legal, and compliance teams translate those decisions into enforceable controls and operating processes.
Do AI guardrails slow down deployment?
They can add latency or review steps to individual workflows. When incorporated early, they often shorten the overall path to production by reducing redesign, clarifying launch requirements, and making approvals easier to complete.
Does every AI agent need the same guardrails?
No. Controls should reflect the agent’s data access, autonomy, action scope, and potential impact. Low-risk internal tools may need lightweight checks. Agents that can alter sensitive records, communicate externally, or commit funds require stronger controls and fuller auditability.
How often should AI guardrails be reviewed?
Review them on a standing cadence and whenever the agent’s model, tools, permissions, users, or business scope change. Cost spikes, policy violations, unusual behavior, and incidents should also trigger immediate review.
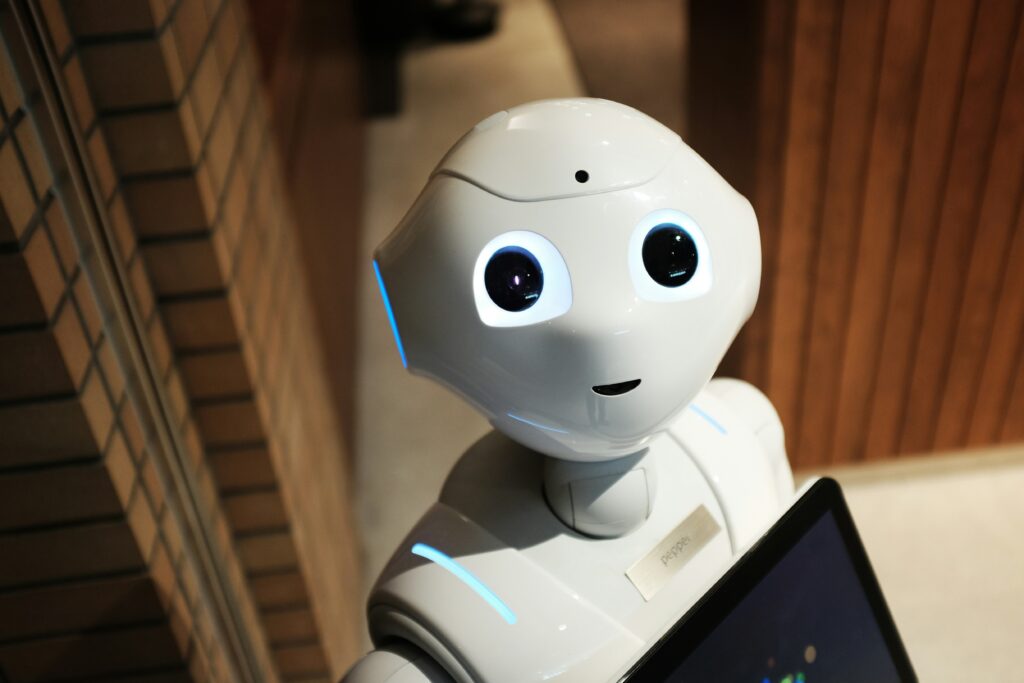 Photo by


 Action from the 11 vs 11 humanoid match at RoboCup 2026. Photo credit: RoboCup Federation.