Scientists have created an ultra-small nanolaser that could eventually allow microchips to transmit information with light instead of electricity, potentially making computers faster while cutting energy use roughly in half. Thousands of the lasers could fit on a single chip, opening possibilities for more efficient data centers, smartphones, and advanced medical sensors.
Researchers have found a way to perform certain quantum operations more than 1,000 times faster, cutting thousands of repeated control cycles down to just one. The advance could reduce errors and bring reliable, fault-tolerant quantum computers closer to reality.
Your AI roadmap is complete, yet no one clearly owns the work of turning it into a production system. Many AI initiatives stall during this handoff.
The artifacts of a serious engagement are in place: mapped processes, prioritized use cases, an approved business case, and a roadmap built around real operating needs. The work behind them was credible enough to earn approval, and the investment made sense. Months later, though, that roadmap is still the clearest result anyone can point to.
Now leadership is asking directly: What actually shipped?
They want to see agents running inside real business processes and evidence that the investment is producing a return. The strategy is complete. The production value is still missing.
The consultants delivered what they promised
You walked away with a clear diagnosis of where the business was breaking down. Process mapping followed the work across teams and systems until the real bottlenecks became visible. What looked like a need for more headcount sometimes turned out to be an approval queue or a missing data field upstream. Hiring more people would have left the bottleneck in place.
Opportunity sizing then tested each use case against the realities of your business. Some ambitious ideas lost ground when the team examined the available data and integration work. Smaller, recurring workflows moved up because their economics were easier to prove. The exercise also surfaced whether the data required for each use case actually existed in a usable form. By the time the roadmap was prioritized, you knew why each use case was there, what outcome it served, and how success would be measured.
The approved business case turned that reasoning into an investment decision. It showed what would change, what it would cost, and when the return should show up. Finance had what it needed to fund the work. The teams responsible for delivery understood what leadership expected them to produce.
The engagement narrowed a broad AI ambition into a plan grounded in how your business actually operates. The roadmap earned approval because the work behind it held up.
The roadmap ends where the production gap begins
You’re holding an approved roadmap with no clear path to production. The production gap is the distance between an approved AI strategy and an agent operating inside a live business process.
Once a use case is approved, the nature of the work changes. Strategy establishes where an agent can create value. Delivery has to determine how that agent will work with your data, systems, permissions, and operating policies. It also has to move through the technical, security, and procurement decisions standing between a recommendation and go-live.
Suppose your roadmap prioritizes an agent that helps resolve supplier disruptions. The process map shows where delays occur and how much they cost. Putting that agent into production introduces a different set of decisions. It needs access to live order data. Operations has to determine when a person must approve its recommendations. If supplier data is missing or a system call fails, the agent needs a defined path back to a person. Strategy may frame these requirements, but delivery has to resolve and implement them.
Your engagement is designed to end before that work begins. Taking the strategy into production requires a different team, contract, and accountability model. When the consultants leave, you have what you commissioned: a credible plan that your organization must now execute.
That is where ownership fractures. The roadmap begins circulating among functions. A technical decision holds up procurement. Once the vendor question is settled, security review becomes the next gate. Everyone continues doing the work assigned to them, but no one owns the handoff or can commit the organization to a production date.
The engagement can finish successfully while the AI initiative stalls. Both can be true. Ownership ended at the same point the work shifted from planning to production.
Your business case has an expiration date
The question leadership is asking is blunt: What is running in production, and what value has it delivered? At this stage, a list of completed activities won’t answer it. Leadership wants to know what the investment has returned.
The original approval committed capital to a measurable change in the business. Consider a supply chain initiative approved to reduce the time required to resolve an inventory exception. The roadmap established the current cost of that delay and the improvement the agent was expected to produce. Until the agent is handling those exceptions inside the live workflow, the expected savings exist only in the business case.
Time now works against the original economics. Internal teams keep committing hours, integration work keeps consuming budget, and the date when the organization begins realizing value moves further out. A business case built around a 12-month payback starts to unravel when the first year passes without an agent processing a live transaction. Delayed benefits and added delivery costs lengthen the payback period and weaken the return leadership originally approved.
The assumptions behind the calculation also start to age. The process evolves while the agent waits, forcing you to validate the expected savings again before asking for more capital. A delay that begins as a delivery problem eventually becomes a funding problem.
You’re far from alone in facing this pressure: 60% of companies see little to no value from AI. This explains why this conversation is happening in so many companies at once. AI spending has moved faster than production results, and leadership has heard enough versions of that story that another quarter of plans and progress updates carries less weight.
A strong roadmap explains why the organization invested. Production results determine whether it keeps investing.
The next deliverable has to be production
Getting an agent into production requires a clear owner who stays with the initiative after the roadmap is approved and has the authority to settle decisions that would otherwise bounce between teams. Their accountability runs through go-live and the first measurable business result.
When a security review stalls the release, your production owner brings the decision makers together and keeps the issue moving until it is resolved. The delay gets reflected in the business case instead of disappearing into a status report. That same person remains accountable when a platform needs to be selected or the operating team needs to prepare for launch.
Production ownership also keeps spending connected to progress. A January 2026 survey of 413 agentic AI stakeholders in regulated industries found that 72% of agentic AI teams had exceeded their expected operating budgets. Without a clear owner, costs accumulate across separate workstreams, while no one can say whether the additional spending is getting the agent closer to production. Your production owner sees the full cost of the initiative and how much work remains. If the economics stop making sense, they can narrow the scope before more capital is committed.
Organizations need to build this production capability into their operating model. When it’s missing, the budget keeps moving while go-live waits for someone to take responsibility.
A second roadmap won’t close the production gap. What closes it is a capability that stays through agent build, integration, and the first live business result, not just the strategy that precedes it. The plan and the execution, under the same accountability.
Finish what the roadmap started
Your consulting engagement did exactly what it was designed to do. It helped you understand which processes to target, what the return should look like, and what success means. The gap isn’t strategy. It’s the execution, integration, and accountability that gets an agent from approved to running.
The roadmap made the investment case. Getting an agent into a live business process is how you begin proving it.
Humans are difficult to simulate. We are quick, complex thinkers, and our exact actions aren't predictable. So how can we sufficiently train robots to collaborate with us?
The head acts as a natural focal point for nearby workers. The lighting interface gives nearby workers an immediate visual indication of Atlas’s operational state, intended actions, and any system warnings.
Humanoid robots, robotic systems with body shapes and limbs resembling those of humans, could potentially assist people with manual tasks in various real-world settings. So far, however, most of these robots can reliably perform only a limited set of movements.
Humanoid robots, robotic systems with limbs and body structures that resemble those of humans, could tackle various manual tasks in homes, workspaces and other settings. Yet teaching these robots to reliably perform different humanlike movements is typically challenging and time-consuming.
Automotive plants have had robots for 40 years and integrators on retainer. Many electronics teams don't have that depth yet, and they're being asked to automate more and at a faster pace.
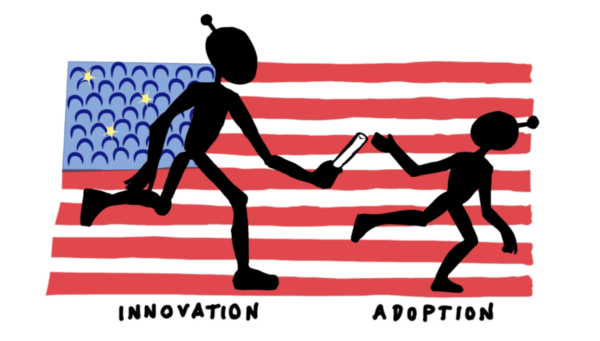
US robotics researchers and industry are looking for a cohesive national robotics strategy that will maintain basic research and innovation while improving domestic production and adoption of robots.
By Ellen H. Rumley and Allison Okamura
A leader in tech innovation
Robots are a crowd-pleasing example of American innovation and global technological leadership. The latest press release of Boston Dynamics’ Atlas executing the ‘Ghost Rabona’ soccer kick highlights the increasingly natural movements of humanoids (1). At the other end of the spectrum, academic researchers are redefining the limits of miniaturization and building robots at the micrometer scale (2). Private and government funding propel foundational research forward, leading to breakthroughs in both hardware and software across U.S. labs and corporations (3, 4). Such progress reaffirms the U.S. as an intellectual and innovative powerhouse, a reputation that carries large geopolitical weight.
But retaining a lead solely in the R&D phase yields diminishing returns if the U.S. fails to manufacture robotic hardware at scale within its own borders. Critics fear this dynamic prevents the U.S. from reaping the economic benefits of the very technology it pioneers (5, 6). Ramping up domestic production will require a heavily coordinated effort between government, industry, and academics – a pivot from traditional U.S. technology strategy.
Free market and military capital
Historically, the U.S. has maintained a laissez-faire approach to technological innovation, allowing corporate and private investors driven by the free market to shape the course of advancement. This innovation-first strategy is largely credited with fueling the growth of global tech giants and the rise of Silicon Valley, which altogether represents roughly 12% of the national GDP (7). America’s leadership in artificial intelligence can be largely attributed to this free-market engine, which prioritizes high projected profit margins and rapid scalability of software (8).
When it comes to U.S. robotics hardware, the Department of Defense/War (DoD/DoW) has stepped in as one of the primary catalysts for innovation and investment. The Pentagon’s fiscal year 2026 budget requested an unprecedented $13.4 billion for developing autonomous systems; a major increase from years prior. The DoD/DoW is requesting an additional $53.6 billion for autonomous systems and drones for 2027 (9). Private capital has quickly mirrored federal priorities; in the first quarter of 2026 alone, defense technology venture capital investments reached a record $19.8 billion. This surge is tightly bound to contemporary geopolitical conflicts, such as the hybrid warfare seen in Ukraine, where the U.S. plays a key role in funding drone production and in recent times deploying humanoids (10, 11). The significant role that autonomous systems have played in conflict zones like the Strait of Hormuz has also signaled the high dependency of strategic military operations on robotics (12).
A bottleneck for domestic manufacturing
While investment in robotic innovation does provide certain economic benefits, it does not support U.S. competitiveness in critical industries – specifically in physical manufacturing. Hardware inherently requires higher, long-term capital expenditures and yields lower short-term financial returns compared to software. Consequently, there could be less incentive to compete against other global manufacturing leaders. Furthermore, while the DoD funds early-stage R&D and specialized military platforms, its mandate stops short of supporting commercial scaling efforts necessary to implement technologies for broader civilian and industrial applications.
As a result, while the U.S. is the third-largest consumer of industrial robotics in the world (with industrial adoption surging by 11% just last year in sectors like logistics, packaging and automotive) (13), it lacks the infrastructure to build what it consumes. While a few prominent U.S. companies do manufacture application-specific robots (some examples being Intuitive Surgical, Amazon Robotics, and Agility), the U.S. mostly relies on foreign imports for baseline industrial robot installations (14). Contrast this with Japan, which relies on foreign imports for a mere 2% of its domestic installations (15).
The systemic under-development in domestic robotic manufacturing leaves the U.S. vulnerable to hardware dependencies and supply chain disruptions. While industrial leaders like Japan and Germany are reliable trade partners, the U.S. government increasingly views hardware dependencies as a national security vulnerability. In recent years, robots have been reclassified as a critical dual-use technology, considered central to 21st century technological sovereignty (16). This reality makes robotics manufacturing a target for foreign adversaries, since foreign supply chains introduce operational chokepoints.
Currently, the U.S. government responds to these vulnerabilities through aggressive export controls and protective procurement policies, which are designed to slow down adversary agendas by blocking their access to the U.S. IP and markets. As one example, in 2021 the President issued the NSPM-33 (a national security memorandum directed to executive agencies) mandating federally funded research institutions to establish strict internal compliance frameworks (17). While designed to allow the continued recruitment of international talent, it enforces rigid vetting protocols on researchers potentially associated with Malign Foreign Talent Recruitment Programs (MFTRP) or of dual national affiliation (18). As another example, in early 2026 lawmakers proposed the bipartisan American Security Robotics Act, a bill designed to ban the federal procurement and operation of unmanned ground vehicles and humanoids manufactured by foreign adversaries, specifically targeting China (19).
Getting by without a government-led national robotics strategy
Rising concerns over robotics supply chain vulnerabilities strongly echo the semiconductor anxieties that originally led to the CHIPS and Science Act of 2022, which marked a historical pivot for the U.S. towards an active state-supported industrial policy (20). Today, there is a similar pressure mounting for the federal government to coordinate a sovereign robotics pipeline via a unified national roadmap.
The challenge facing the U.S. does not seem to be a lack of federal funding, but rather how the funding is distributed across multiple agencies with different mandates (21). The National Science Foundation funds basic academic research; Department of Energy runs national research laboratories and funds external research programs developing robotics relating to energy infrastructure; National Institute of Health supports and conducts medical robotics research; NASA funds and develops robotics for space applications; the ARM Institute supports domestic manufacturing initiatives while satisfying dual-use funding criteria through the DoD/DoW; and DARPA funds robotic innovations relevant to national security. (The latter organizes the well-known DARPA Grand Challenges, robotics competitions for fueling research bridging fundamental science and military applications.) Because federal investments from these programs and agencies are confined to isolated, mission-specific niches, the U.S. remains one of the few leading industrial nations without a centralized robotics strategy.
This structural fragmentation may soon change as political attention shifts towards treating robotics as a critical sector (22). In 2025, four state representatives re-launched the bipartisan Congressional Robotics Caucus as a platform for members of Congress to stay informed over the diverse issues surrounding robotics policy (23). In June 2026, legislators formally introduced the bipartisan National Commission on Robotics Act, which calls for an independent commission of 18 robotics experts tasked with providing evidence-based policy to accelerate domestic development (24). This legislative momentum is reinforced by a series of recent Executive Orders (mandates from the US President) demanding a high-level federal coordination including the Unleashing American Drone Dominance Order (25), the Golden Dome for America Order (26), and the Launching the Genesis Mission Order (27).
Robotics strategies from non-government actors
In the absence of a centralized federal initiative, stakeholders in industry, NGOs, and academia are self-organizing and publishing their own robotics frameworks recommendations for the United States.
In 2025, A3 (Association for Advancing Automation) released their Vision for a U.S. National Robotics and Automation Strategy (28), which argues that the future of U.S. leadership in artificial intelligence is inextricably linked with its global robotics leadership. A3 provides actionable policy items, such as the formation of a governmental robotics office for coordinating federal robotics initiatives, the establishment new standards for nascent robotic hardware and software, and the introduction of tax incentives for rapid robotics adoption and creation of worker training programs.
Complementing these industry goals, in 2025 the nonpartisan thinktank, Special Competitive Studies Project (SCSP), has released their Memos to the President – National Robotics Strategy (29). This document couples the call for mass industrial robotics adoption with recommendations for more aggressive trade restrictions on Chinese technologies. Following this publication, SCSP launched its National Security Commission on Robotics for Advanced Manufacturing for implementing this comprehensive strategy; members include industry and academic players including GM, Boston Dynamics, Nvidia, AMD, the University of Michigan and MIT’s Industrial Performance Center (30).
Academics have similarly spearheaded their own national strategies. Once every four years, academics led by Professor Henrik Christensen (UC San Diego) publish a roadmap for U.S. robotics (31). Past editions directly catalyzed the creation of the National Robotics Initiative (NRI), a multi-agency federal program running from 2012 to 2022 that supported foundational research on robotics, specifically promoting collaborative robots for working alongside humans. (Christensen also recently published Global Robotics Technology Roadmap 2025–2035, an independent positions paper synthesizing government and industry strategies across Europe, Asia, and the United States (32).)
All three stakeholders share a common motivation for a national robotics strategy: the nation’s population and workforce are declining; There is a surplus of jobs fulfilling the 3 Ds (dull, dirty, dangerous); Robotics should become a national priority once more. In addition to funding and incentives, authors also discuss the need to consider the impact of technology on the workforce – a topic of large structural tension, with fear of robots displacing jobs and particularly outcompeting blue-collar and immigrant workers (33, 34). Christensen et al. delve deeper into the psychology of the workforce, and recommend a framework which balances technological growth with worker empowerment. They propose that prioritizing human-centered collaborative robots and wearable devices could shift the robotics narrative from a source of widening economic disparity towards heightening workplace satisfaction and production efficiency. However, recent mass layoffs amidst installations of collaborative robots reveal the complexity of this balancing act (35).
The U.S. is in the midst of a major shift regarding how it shapes robotics advancement. Because a formal federal strategy does not yet exist, private and academic stakeholders are proactively drafting the blueprints themselves. Consolidating these ideas into a unified national policy will have far-reaching consequences for national security, geopolitical influence, labor markets, and manufacturing sovereignty. The world watches carefully as this shift unfolds.
Thanks for reading. For our next article we will be delving into China’s national robotic strategies – stay tuned.
Ellen H. Rumley – Policy Analyst
Allison Okamura – Vice President
IEEE RAS Science & Technology Watch Board
References
Boston Dynamics and Hyundai. School of Football | The Ghost Rabona | Boston Dynamics x Hyundai. YouTube, 2026.
University of Pennsylvania School of Engineering and Applied Science. “Penn and UMich Create World’s Smallest Programmable Autonomous Robots.” Penn Engineering Today, 2024.
“7 Cool NSF-Funded Robots That Are Advancing Science and Helping Society.” S. National Science Foundation, 7 Apr. 2021.
“AI 50 List: Top Artificial Intelligence Companies.” Forbes, 2026.
Atkinson, Robert D. A Time to Act: Policies to Strengthen the US Robotics Industry. Information Technology and Innovation Foundation (ITIF), 2025.
Association for Advancing Automation (A3). Policy Recommendations and Advocacy Principles for the U.S. Automate.org, 2025.
Consumer Technology Association. “Tech Sector Supports 18 Million US Jobs, Represents 12% of GDP, Says CTA.” CTA Press Releases, 2026.
Brookings Institution. Hardware and Software: A New Perspective on the Past and Future of Economic Growth. Brookings, 2024.
United States Department of Defense. Comptroller Budget Materials: Fiscal Year 2026. 2025.
National Science and Technology Council. Guidance for Implementation of National Security Presidential Memorandum 33 (NSPM-33). Jan. 2022.
White House Office of Science and Technology Policy. Guidelines for Foreign Talent Recruitment Programs. Feb. 2024.
United States, Congress, House. American Security Robotics Act. 119th Congress, H.R. 8189. Government Publishing Office, 2026.
Center for Strategic and International Studies. Innovation Lightbulb: Tracking CHIPS Act Incentives. CSIS, 2025.
Center for Strategic and International Studies. “Why the United States Needs Robots to Rebuild.” CSIS Strategic Technologies Blog, 2025.
Politico Pro Staff. “White House and Congressional Frameworks Shift Toward AI and Robotics.” Politico, 3 Dec. 2025.
United States, Congress, House of Representatives. “McGovern, Latta, Stevens, Obernolte Announce Re-Launch of Congressional Robotics Caucus.” Office of Congressman Jim McGovern, May 2025.
United States, Congress, House. National Commission on Robotics Act. 119th Congress, June 2026, H.R. 7334.
S. Army News Service. “Drone Dominance Program Receives First Order; Gauntlet II Gets Underway.” Defense Department News, 2026.
Congressional Budget Office. Cost Estimate and Analysis of the Golden Dome Air Defense Framework. May 2026.
S. Department of Energy. “Energy Department Advances Investments in AI and Robotics for Scientific Discovery.” DOE News, 2025.
Association for Advancing Automation. “A3 Policy Recommendations and Advocacy Principles for the U.S.” April 2024.
Special Competitive Studies Project. Memos to the President: National Robot Strategy. SCSP, 2025.
“Boston Dynamics Joins U.S. Robot Strategy Think Tank Led by Ex-Google CEO.” Seoul Economic Daily, March 2026.
Christensen, Henrik, et al. Robotics for a Better Tomorrow: 2024 US National Robotics Roadmap. UC San Diego / Academic Coalition, 2024.
Christensen, Henrik. Global Robotics Technology Roadmap 2025–2035. Independent Position Paper, 2025.
Appelbaum, Binyamin. “What Replaces Deported Immigrant Workers? Not Americans.” The New York Times, Feb. 2026.
Pew Research Center. “Key Findings About How Americans View Artificial Intelligence and Automated Systems.” Pew Short Reads, 12 Mar. 2026.
“Unions Furious as GM Replaces 1,000 Factory Zero Workers with 50 Robots.” Yahoo News, June 2026.
A research group comprising Associate Professor Yoshihiro Nakata and Taisei Mogi from the Graduate School of Informatics and Engineering at The University of Electro-Communications (UEC), Japan, and Mari Saito of Sony Corporation has developed MOFU (MOrphing Fluffy Unit), a mobile robot capable of whole-body expansion and contraction. The group investigated how whole-body expansion-contraction affects perceived animacy, or the extent to which the robot is perceived as lifelike. In addition to expansion-contraction and locomotion, MOFU was designed with features including quiet operation and a soft, fluffy exterior. The study was published in PLOS ONE.
When an AI agent causes harm, leaders must be able to defend why it was allowed to act. To a board, auditor, or regulator, they need to show that the agent’s permissions, controls, and approvals were matched to the consequences of failure.
Treating guardrails as an on/off switch hides that decision. Guardrail risk tiering makes it explicit: every agent clears a common baseline, then receives stronger controls as its access, authority, and potential harm increase.
A read-only internal agent creates far less exposure than one that can access regulated data, invoke privileged tools, send external communications, or modify a system of record. The level of oversight applied to each should reflect that difference.
Key takeaways
Guardrail risk tiering matches oversight to business exposure. The strongest controls belong where an agent’s access and authority create consequences the organization would struggle to contain or reverse.
Every agent needs controls at its input and output boundaries. Inputs include user prompts and untrusted content introduced through retrieval, APIs, tools, and other agents.
An agent’s authority determines what leaders may have to defend. Sensitive data access, external communications, system changes, and financial transactions require closer oversight.
High-impact actions need hard stops outside the model. Transaction limits, permissions, approved recipients, and required approvals should be enforced before execution.
Guardrail risk tiering continues throughout the agent lifecycle. New tools, permissions, data sources, and autonomy can change an agent’s exposure after deployment.
Why your exposure should set the guardrail level
Your organization already makes proportional access decisions. Role-based access control (RBAC), OAuth, data classification, and access policies determine who can reach a system, what they can see, and what they can change. Agent guardrails extend that risk logic into runtime execution.
Guardrail risk tiering is the practice of matching the depth and placement of runtime controls to an agent’s data access, tool permissions, action authority, and potential consequences.
An agent’s exposure can change as a workflow unfolds. Reading an approved document carries one level of risk. Passing information into a tool that updates a customer record or initiates a transaction raises the stakes. Each new permission expands the set of outcomes the organization may have to explain after an incident.
Start with a common baseline. Add enforcement where the agent gains access to sensitive information or the authority to produce consequential outcomes. Guardrails reduce the probability and impact of unsafe behavior, but no set of controls can prevent every failure.
The leadership responsibility is to show that the level of oversight was deliberate, proportional, and approved before the agent acted.
Set the floor every agent has to clear
Every agent needs controls around information entering the workflow and consequential content leaving it.
The initial user request is only one input boundary. Once an agent begins retrieving documents, scraping pages, calling APIs, interacting with tools, or exchanging information with other agents, each result becomes another source of potentially untrusted input. A retrieved document or tool response can contain malicious or conflicting instructions just as a user prompt can. This is the indirect prompt injection surface that boundary controls need to cover.
Keeping unsafe instructions from shaping execution
Keeping sensitive information from leaving the workflow
Inspect user prompts, retrieved documents, scraped content, API responses, tool results, and other external context for prompt injection, prohibited content, sensitive information, and policy violations before that information influences execution.
Inspect consequential outputs for personally identifiable information (PII), toxic or biased content, sensitive data, and other policy violations before the response reaches a user or downstream system.
For a read-only internal agent working with approved information, these controls may cover most of the relevant exposure. Once an agent invokes privileged tools or takes action, boundary checks alone leave gaps between what the agent receives and what it ultimately does.
Leaders should know where those gaps begin because that is where the organization’s accountability expands.
What you’ll need to explain when something goes wrong
Once an agent moves beyond read-only tasks, its tools become one of the clearest indicators of business exposure. Write access to production databases, external communications, financial transactions, code execution, and sensitive personal data all increase the consequences of a bad decision.
For higher-risk tools, guardrails should evaluate proposed actions before execution. Failed checks need a defined response, such as blocking the action, using a safer fallback, or escalating to an authorized person.
The organization also needs a record of which tool was called, what permissions were active, which policy checks ran, and what changed downstream. Without that evidence, leaders may know that something went wrong without being able to explain how the agent was authorized to do it.
To determine how deep those controls should go, evaluate each agent against five questions:
What data can it access? Public or already-classified information creates a different exposure than customer, financial, HR, healthcare, or other sensitive data.
What can it write, execute, or trigger? Read access carries less operational authority than permission to modify a system of record, execute code, contact a customer, or initiate a transaction.
What authority does it operate under? Broader permissions and elevated access increase the range and severity of actions available to the agent.
How reversible are its actions? A generated summary can usually be discarded. A payment, deleted record, changed entitlement, or external communication can be far harder to unwind.
How far can a failure propagate? An isolated error carries a different risk profile from an action that affects downstream systems, customers, business processes, or other agents.
These questions turn a technical inventory into a leadership decision about the consequences the organization is willing to accept.
Decide which actions need a hard stop
Model-based checks work well when a control requires interpretation. They can identify prompt injection, unsafe content, off-topic behavior, or context-dependent policy violations.
Hard business constraints require deterministic enforcement outside the model. Before a high-impact tool executes, policy checks can validate permissions, transaction limits, approved recipients, required fields, data classifications, allowlists, and approval requirements.
The model can propose an action. A deterministic policy decides whether the action is permitted. When the consequences are difficult to reverse, an authorized person may need to make the final decision.
Spend oversight where failure costs the most
Every policy check consumes time, computing resources, or human attention. Leaders need to allocate that oversight according to exposure.
A low-risk summarization agent may need lightweight input and output checks. Multiple approval gates would consume review capacity while covering risks the agent does not create.
An agent that modifies customer records, communicates externally, or initiates transactions presents a different calculation. Validating permissions and proposed actions adds time, but the alternative may involve an unauthorized write, data exposure, investigation, remediation, or regulatory scrutiny.
Guardrail risk tiering makes that allocation explicit. The strongest enforcement belongs where a failure would be hardest to contain, reverse, or explain.
A practical way to allocate oversight
Enterprises don’t need to adopt a universal taxonomy. The objective is to connect an agent’s actual capabilities to a corresponding level of enforcement.
A practical guardrail risk tiering model might look like this:
Risk tier
Typical agent capabilities
Recommended guardrail depth
Baseline
Read-only access to approved or low-sensitivity data with no consequential actions
Input, retrieval, and final-output checks
Elevated
Sensitive data access, external communications, or tools that affect downstream workflows
Baseline controls plus tool-level policy enforcement, scoped permissions, and detailed tracing
High impact
Writes to systems of record, financial transactions, code execution, or difficult-to-reverse actions
Baseline and tool-level controls plus deterministic policy checks, explicit escalation paths, human approval where required, and complete auditability
Giving an existing agent write access, connecting a new Model Context Protocol (MCP) server, or expanding its data permissions can change its risk profile even when the model and prompt remain the same.
Guardrail risk tiering continues throughout the agent lifecycle. Each change in access, tools, or autonomy should trigger a decision about whether the organization can still defend the existing level of oversight.
Build a record you can defend
A risk tier has little value if nobody can show who assigned it, what controls it requires, or who can intervene. Before an agent reaches production, create a governance record that a board, auditor, regulator, or incident-response team could examine.
Name the accountable owner and approving authority. Identify who owns the agent’s performance and risk, who approved its operating scope, and who can change or revoke that approval.
Document what the agent is authorized to access and do. Record the data, tools, APIs, and downstream systems it can reach, along with what it can read, write, execute, or trigger.
Record the risk tier, controls, and rationale. State why the agent received its classification, which input, output, and tool-level controls apply, and who signed off on the decision.
Define hard stops and escalation authority. Specify which actions require deterministic enforcement or human approval. Name who can investigate, restrict permissions, initiate takeover, roll back a release, or suspend the agent.
Set review triggers and evidence requirements. Define what must be retained for audit and investigation. New tools, broader permissions, different data sources, and greater autonomy should trigger reassessment.
This record gives leaders more than proof that controls exist. It shows how the organization connected authority to oversight and who accepted responsibility for that decision.
Know whether the controls are working
Assigning a risk tier establishes the required controls. Leaders still need evidence that those controls operated as intended.
That evidence comes from tracing tool calls, identity and permission context, policy decisions, downstream actions, and escalation events. A tool call may satisfy a technical interface while violating a business rule. An action may execute under the wrong permission context. An agent may repeatedly encounter conditions that should trigger human review.
These patterns become visible when the organization can follow behavior across the execution path. The resulting record helps leaders answer specific questions: Which identity authorized the action? Which policy applied? Did the agent receive an exception? Who was notified? What changed downstream?
Leaders need evidence they can produce during an audit or after an incident — not a description of the controls that were supposed to run, but a record of what actually happened.
Guardrail risk tiering is a method for matching the depth and placement of runtime controls to the risk created by an AI agent’s data access, permissions, tools, actions, and downstream impact. Higher-risk capabilities receive additional controls closer to the point of execution.
What guardrails should every AI agent have?
Every agent should have a minimum set of controls around information entering the workflow and consequential content leaving it. Input controls should cover the original user request as well as retrieved documents, API responses, tool results, and other untrusted context introduced during execution.
When does an AI agent need tool-level guardrails?
Tool-level controls become increasingly important when an agent can access sensitive data, write to systems of record, communicate externally, execute code, initiate transactions, or trigger other consequential workflows. Higher-impact actions may also require deterministic policy enforcement or human approval before execution.
Do AI guardrails eliminate agent risk?
No. Guardrails reduce the likelihood and potential impact of unsafe or unauthorized behavior. Teams still need appropriate permissions, observability, testing, auditability, escalation procedures, and ongoing review to manage residual risk.
When should an agent’s guardrail risk tier be reassessed?
Reassess guardrail risk tiering whenever the agent gains new tools, permissions, data sources, workflows, or autonomy. Changes to connected systems can alter risk even when the model, prompts, and core agent logic remain the same.
Today’s solutions are designed to reduce the complexity of deployment with standardized, configurable automation platforms that warehouses can get up and running — sometimes in as little as a day — with little to no software engineering required.
Waving flags, "chanting" slogans and marching in circles, around 30 robots took to the streets of Warsaw on Monday to campaign for AI regulation in front of the Polish digital affairs ministry.
New BBC sitcom Ann Droid imagines a near future in which robots provide care and companionship to older people at home.
The series centres on Sue, a recent widow played by Sue Johnston, her hapless son Michael and Linda, an assistive care robot played by Diane Morgan. Linda is designed to provide daily support and companionship, with predictably comic results.
As researchers in social care, ageing and human-centred robotics, we obviously watched Ann Droid with a keen eye. Beneath the jokes are questions that researchers are already tackling.
Could robots help address loneliness among older people? Can a machine provide companionship without replacing human connection? While the series exaggerates what robots can currently do, some of the technology it depicts is already being tested.
The BBC’s Ann Droid sitcom.
A social enterprise in south-west England has been piloting Comfort Companions in partnership with Age UK South Gloucestershire. AI-generated personas offer conversation and guidance to older people living alone and at risk of loneliness.
It runs alongside Age UK’s volunteer programme, with befrienders helping older people learn how to use the app. The AI companions are intended to supplement the waiting list for human befrienders rather than replacing them.
Physical robots are being tested too. West Berkshire Council has been running a trial using robotic pets in its care homes.
Neither scheme offers robots who look like Linda. Current systems tend to be AI avatars on a screen or robotic cats or dogs, or speakers that provide a voice in the room. They do much less than Linda too. They can’t help someone up after a fall, wash them or get them dressed.
What technology does currently do best is monitoring and prompting. Systems that can detect a fall and alert another person are far more mature, while technology can also encourage someone to contact friends, make a phone call, or get out of the house.
Can a machine make you less lonely?
It’s worth considering this distinction because loneliness is not simply the same as being alone. It’s a personal feeling that our relationships are insufficient, accompanied by a desire for more or better social contact.
A robot companion, therefore, is unlikely to solve loneliness simply by being present. What matters is the quality of the interaction and whether technology can help someone maintain relationships with the people who matter to them.
This is one of the more interesting ideas in Ann Droid. Linda can sometimes strengthen Sue’s existing relationships rather than replace them, encouraging her to meet friends and plan activities outside the home. That’s potentially a more useful way to think about companion technology. The goal need not be to create an artificial friend who substitutes for a human one, but to help people remain connected to others.
The barriers are still substantial. Battery life is a limitation. Most humanoid robots manage between 90 minutes and five hours per charge when new. This is why an overnight camping trip featured in the sitcom is a fair test on the fantasy.
Robots are much better at some tasks than others. A machine may be able to play chess, for example, but picking up an unfamiliar household object in the real world remains surprisingly difficult.
The social barriers are even harder. Robots struggle with the social subtleties that people take for granted. Systems that learn by copying human behaviour can reproduce an action without understanding its intention. They also cannot reliably interpret facial expressions.
A review of systems designed to detect emotion from faces found that they performed worst when interpreting older faces, with anger and neutral expressions among the least reliably identified. This is important in care because recognising how someone is feeling can be crucial.
Would we trust a robot carer?
Ann Droid also plays on a more instinctive discomfort: should we trust a machine that’s designed to look after us? The sitcom playfully touches on public worries about interacting with robotic companions, including people’s distrust and worries about potential harms. For example, in one episode two robots enjoy a joke together about killing their human companions.
Research suggests that older people can see value in companion robots. But acceptance depends partly on whether people feel they remain in control. And appearance is a factor too.
In 1970, the roboticist Masahiro Mori proposed the idea of the “uncanny valley”. As machines become more human-like, we initially respond more positively to them. But when they look almost human without quite getting there, that warmth can turn into discomfort.
Ann Droid – dinner with the robot-in-law.
Robots have some obvious advantages. They don’t get bored, tired or impatient. They can handle dangerous tasks and they’re available at 3am. But they can’t provide something fundamental to care: a relationship in which both people choose to be there.
That’s the bond that no machine can supply. Robots may have a useful role in social care, but they’re worth having only when people want them, alongside human care and companionship. Otherwise, we risk finding an expensive technological answer to a much harder question: why do some older people have so little human contact in the first place?
 US robotics researchers and industry are looking for a cohesive national robotics strategy that will maintain basic research and innovation while improving domestic production and adoption of robots.